Platform overview
One record underneath every control.
CoreGuardian reads the tools you already run, reconciles them into one record per asset and identity, checks each control against policy, and turns the result into a ranked list and audit evidence.
Read-only · No agents · 30+ connectors · 12 frameworks
Three jobs
See it. Fix it. Prove it.
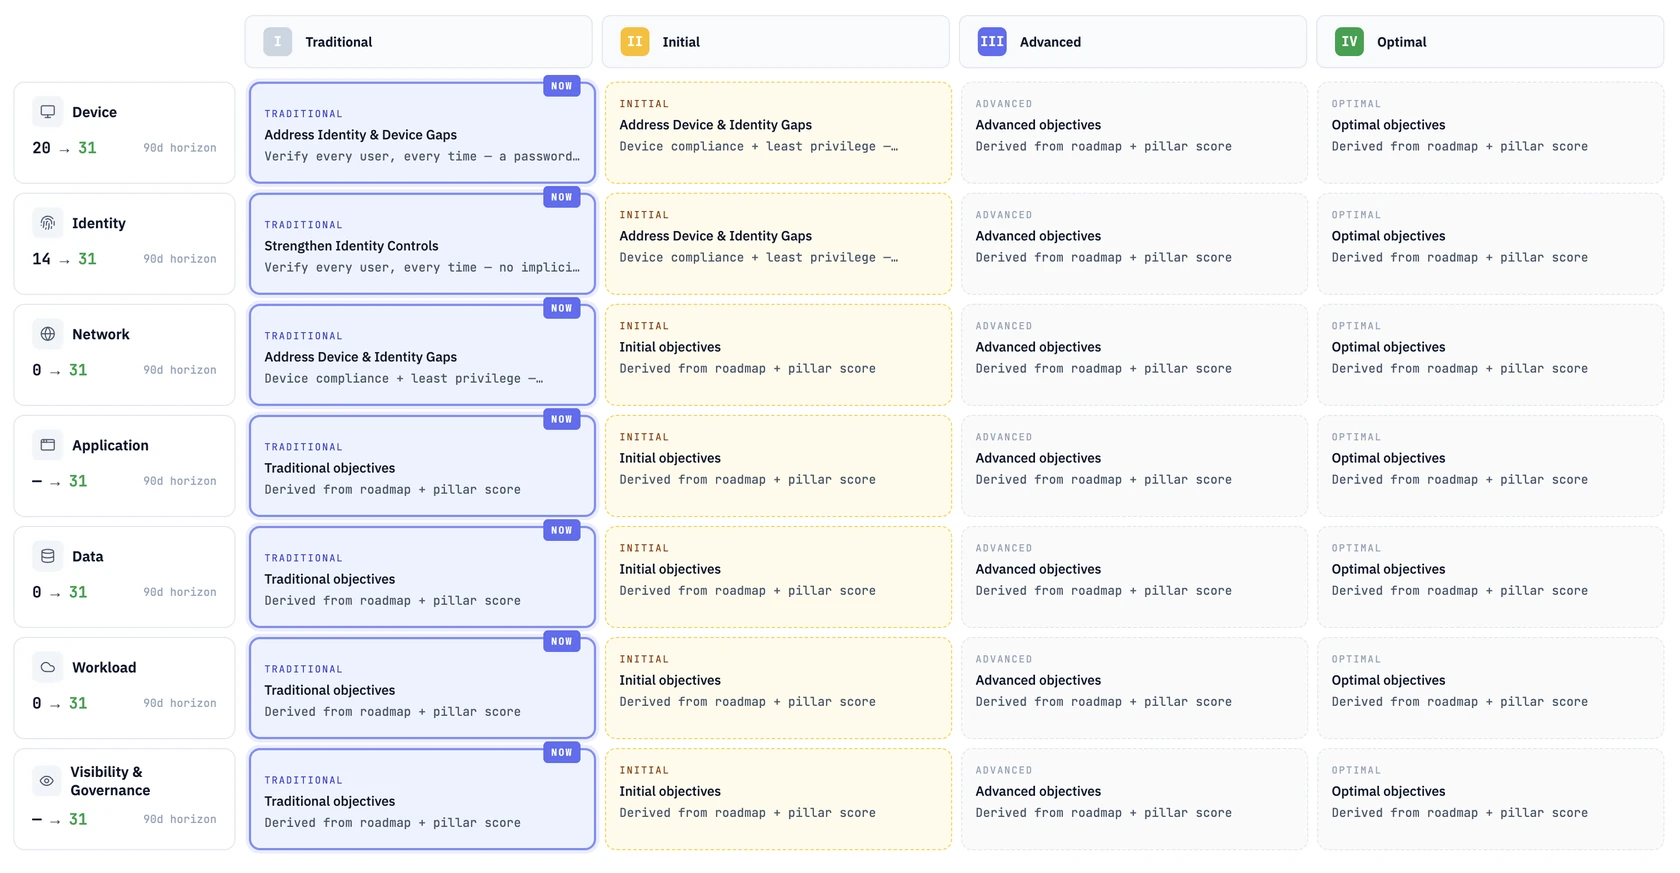
Verify every control, continuously.
- One reconciled record per asset and identity across 30+ connectors.
- Cross-tool contradictions surface as findings: Okta says authenticated, CrowdStrike says the agent is stale.
- Zero Trust maturity per pillar from live connector signal, not a survey.
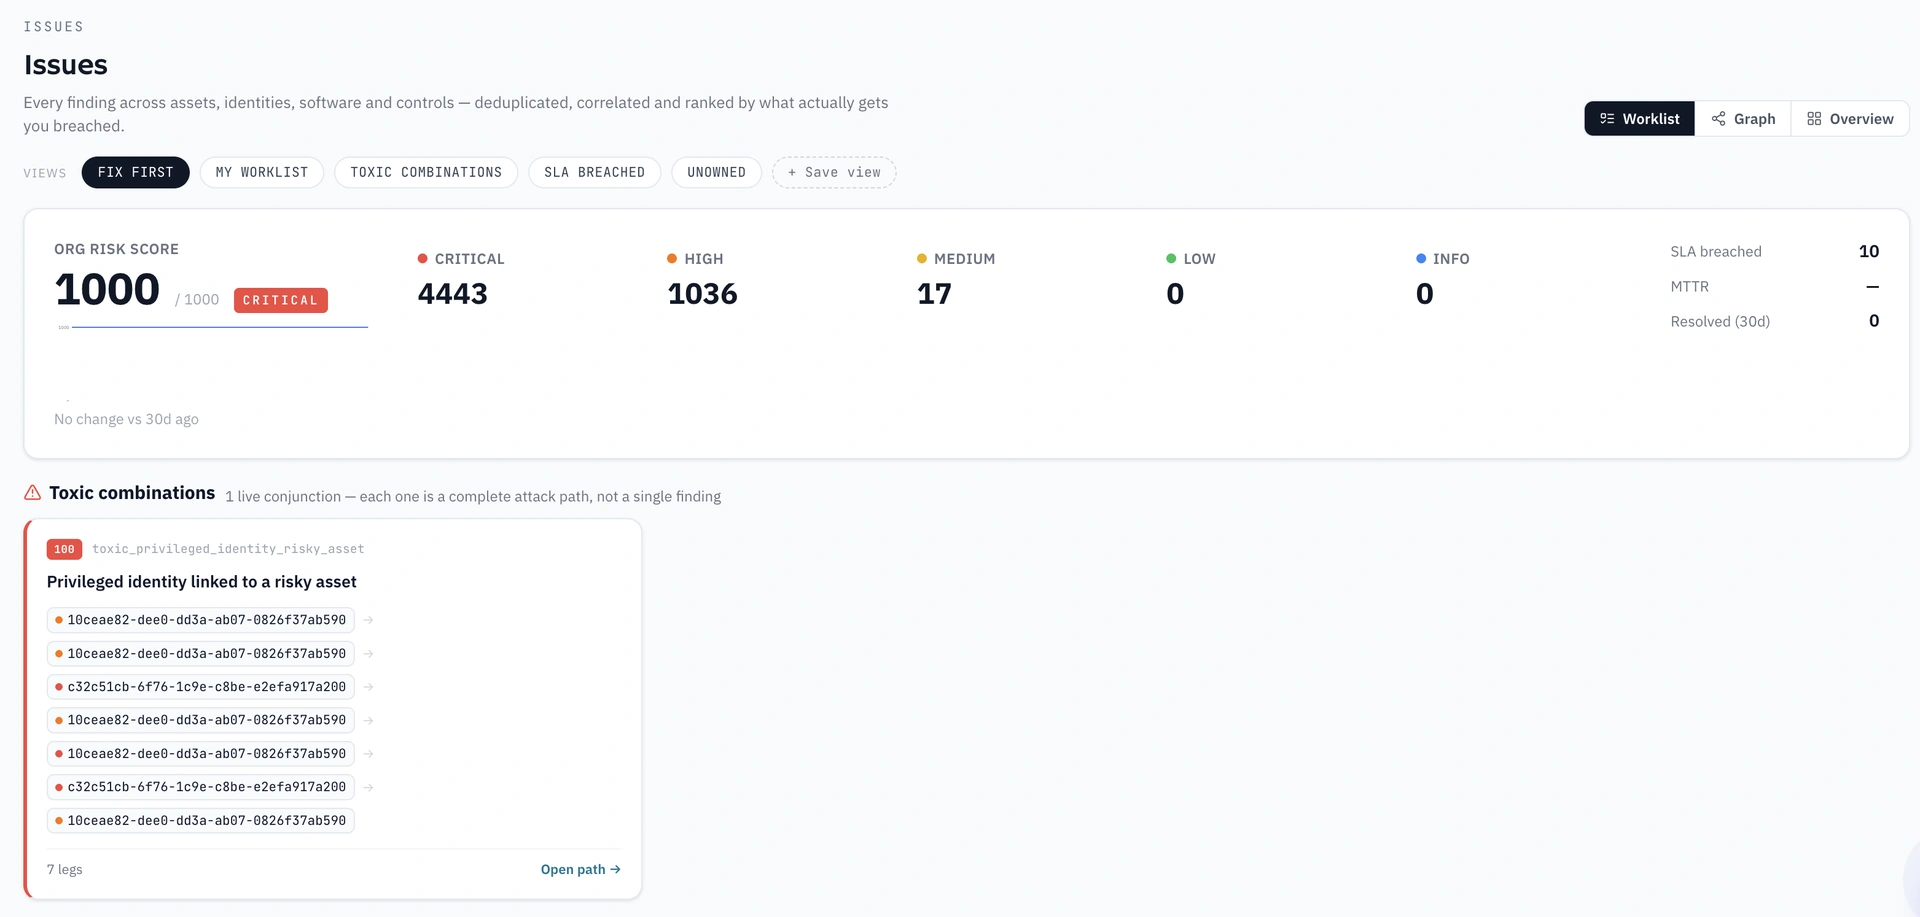
Rank by business risk, not CVSS.
- Criticality, exposure, privileged-identity reach, compliance scope and KEV/EPSS feed one contextual score.
- The result is a short list. Each item has an owner.
- Ranked, owned, and tracked to closure through POA&M.
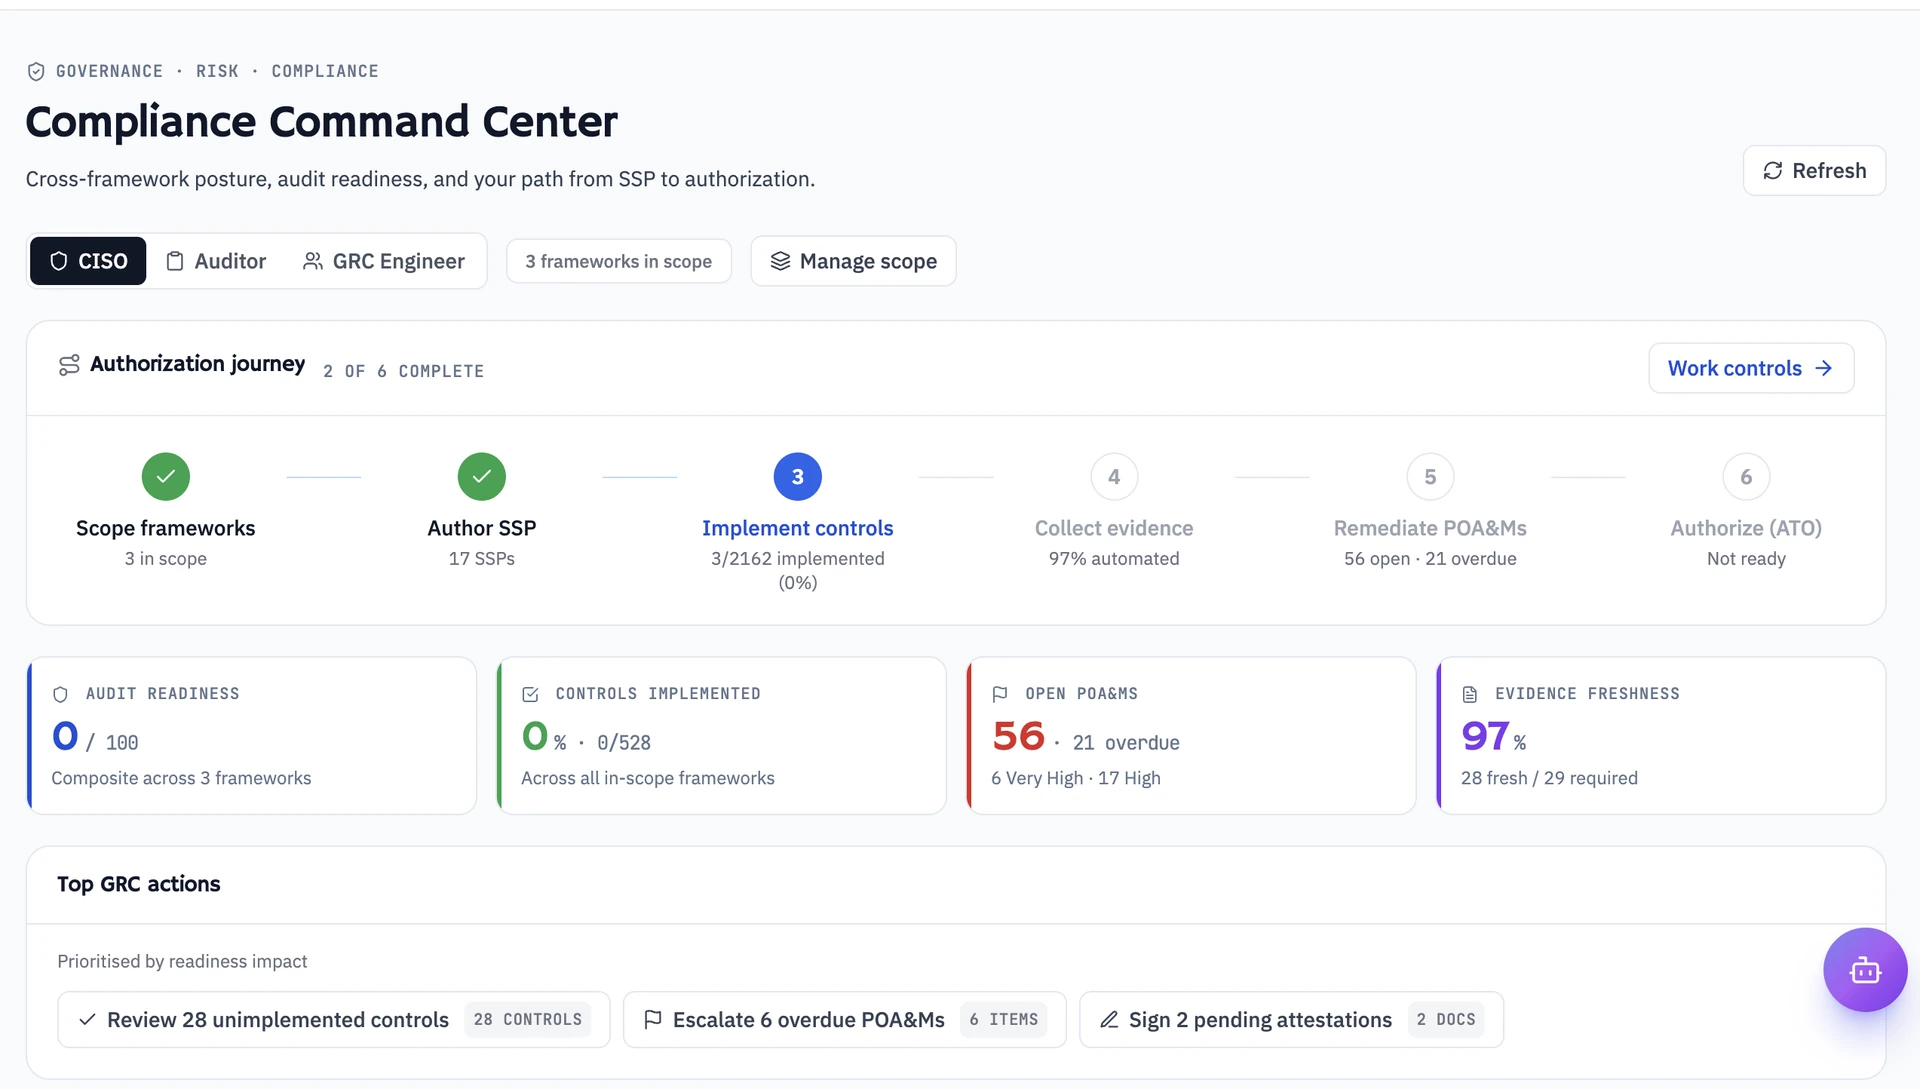
Evidence is a by-product, not a project.
- The data that drove the fix is the evidence: OSCAL SSP, POA&M, SAP and SAR export.
- A tamper-evident evidence locker your assessor can check.
- Cross-framework mapping across 12 frameworks, with the RMF lifecycle and ATO tracking.
How it works
Four steps. Nothing to rip out.
- 01Connectors
Connect
Read-only API connections to the tools you already run. No agents to deploy.
- 02Golden record
Verify
Every source reconciled into one record per asset and identity. Control state checked against policy. Contradictions become findings.
- 03Risk engine
Prioritize
Business context, exposure and live exploitation data rank the few problems that matter, each with an owner.
- 04Evidence locker
Evidence
The same facts become OSCAL SSPs, POA&Ms and framework mappings, held in a tamper-evident locker.
Capabilities
Six jobs, one record underneath.
Exposure & Risk Prioritization
A short list, ranked by what the business stands to lose.
Learn moreIdentity & NHI Security
Every identity, human and non-human, with the keys it holds.
Learn moreZero Trust Posture
Maturity across the CISA ZTMM pillars from live data, not a survey.
Learn moreContinuous Compliance & ATO
Audit evidence produced by your security data, across 12 frameworks.
Learn morePQC Readiness
Know where your crypto debt is before the deadline finds it.
Learn moreAI Agent Governance
Every AI agent in your enterprise, inventoried and governed.
Learn moreWhere the boundary sits
What we do, and what we don’t.
We’d rather you hear it from us than find it in a demo.
- Read. Read-only connections to 30+ tools. We never need write access.
- Reconcile. One record per asset and identity, with contradictions raised as findings.
- Rank. A contextual score and a short, owned list, tracked to closure.
- Prove. OSCAL SSP, POA&M and framework mappings from the same data.
- Change your environment. We never write to your tools. Fixes stay with the teams who own them.
- Replace your stack. Your scanners, EDR and IdP keep doing their jobs. We verify they are.
- Promise what isn’t shipped. Ask us about the roadmap in a demo.
30+ connectors
Works with the stack you already own.
 Microsoft Entra ID
 Okta
 Google Workspace
 SailPoint
 Ping Identity
 AWS
 Microsoft Azure
 Google Cloud
 Wiz
 CrowdStrike Falcon
 Microsoft Defender for Endpoint
 Tanium
 Palo Alto Networks
 Cloudflare Zero Trust
 Zscaler ZIA
 Tenable Vulnerability Management
 Qualys
 GitHub
All product names and trademarks are the property of their owners. Use does not imply endorsement.
One source of truth. Zero blind spots.
See the platform on a stack like yours.
Read-only. No agents. Nothing to rip out.
Request a demo