Zero Trust Posture
Zero Trust maturity from live data, not a survey
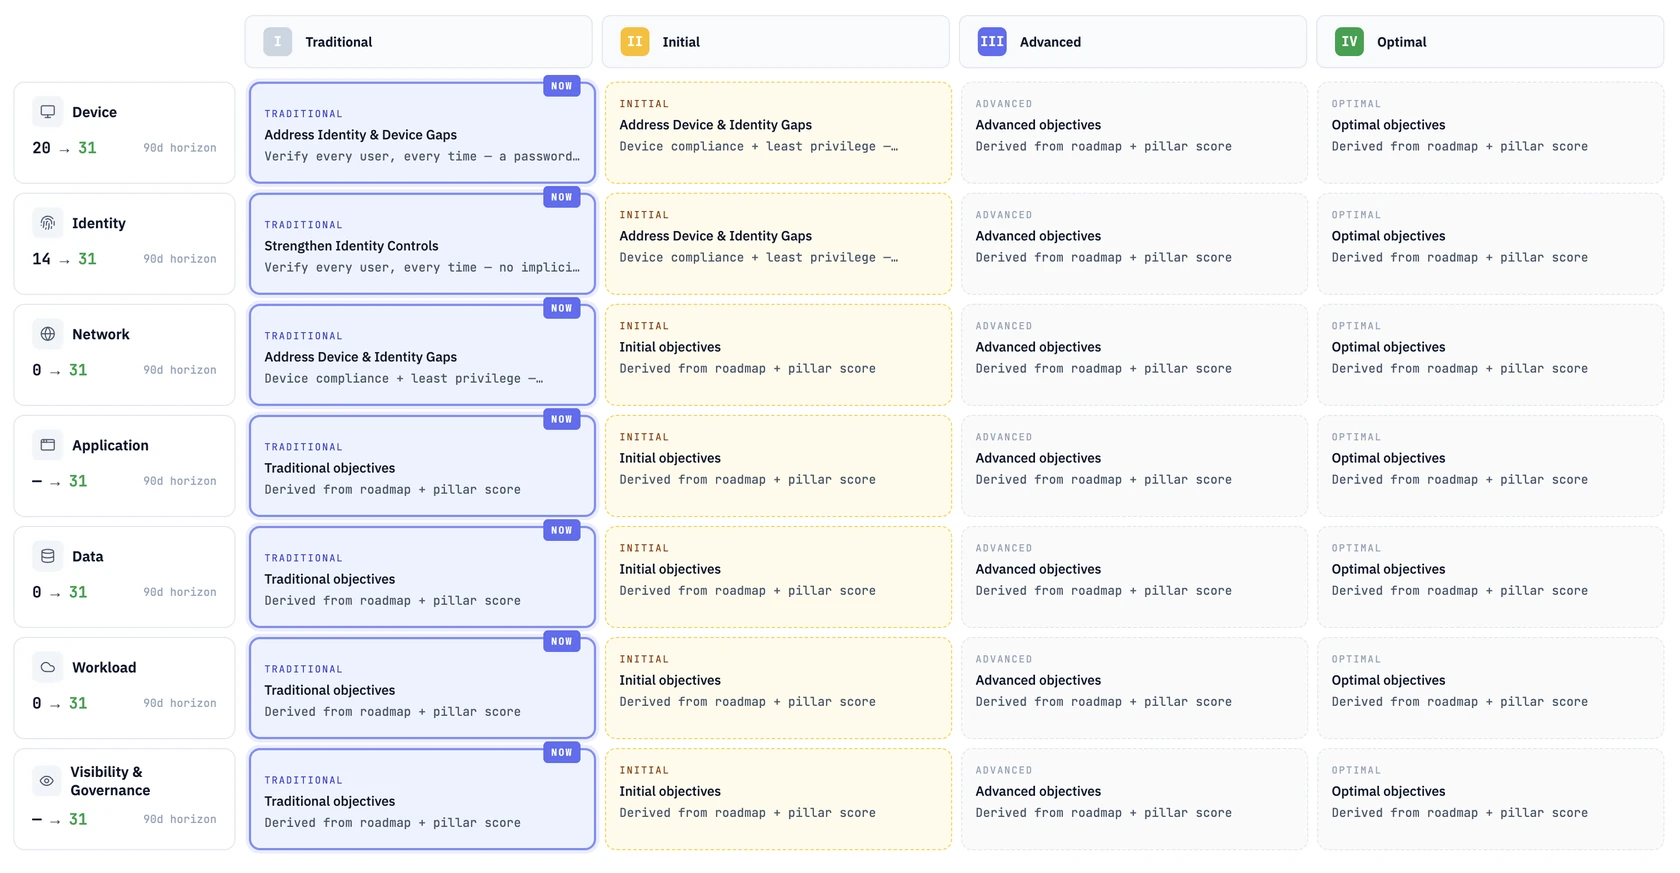
Pillars mapped to the CISA Zero Trust Maturity Model from the tools you already run — with gaps you can assign and export.
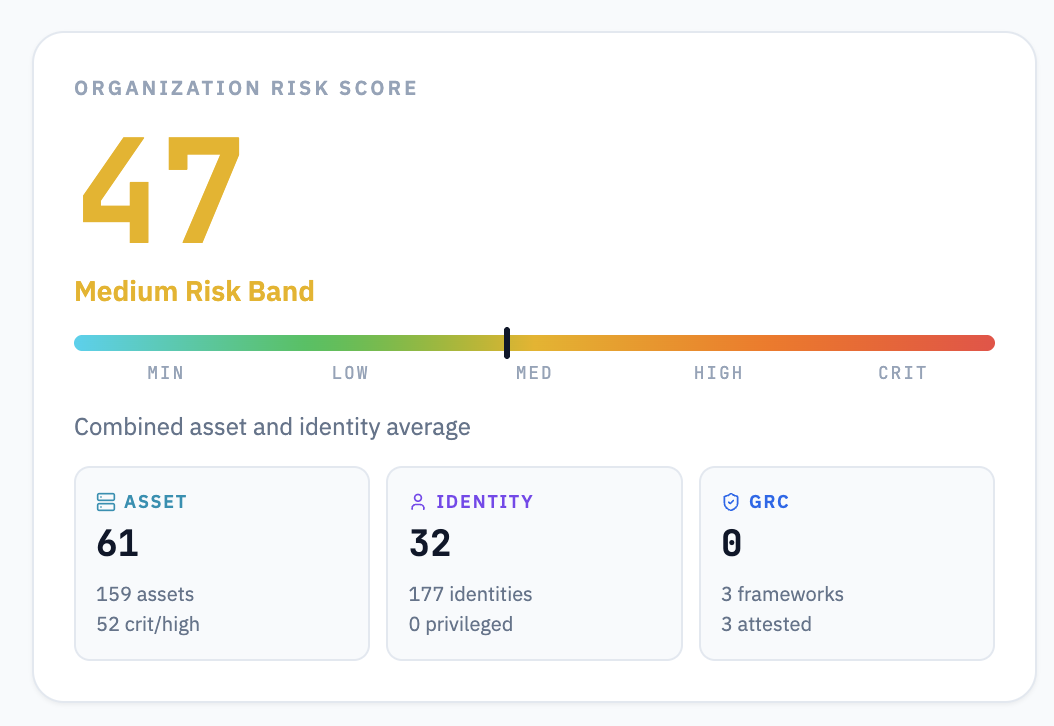
Live signal
Maturity from connector data, not a one-time questionnaire.
Seven pillars
Mapped to CISA ZTMM stages your team already reports against.
Actionable gaps
Gaps your owners can assign, not another maturity slide.
Exportable
Self-assessment exports for the reports you already write.
01
Pillar posture from the stack you own
- Identity, device, network, application, data, visibility, automation
- Vendor-neutral evaluators where signal exists
- Honest about coverage — maturity from live signal, pillar by pillar
02
From score to owned work
- Gap analysis your team can assign
- Exports for Word, JSON, and OSCAL POA&M formats
- Complements — does not replace — your Zero Trust program
Connects to
Works with the stack you already own
- Microsoft Entra ID
- Okta
- Google Workspace
- SailPoint
- Ping Identity
- AWS
- Microsoft Azure
- Google Cloud
- Wiz
- CrowdStrike Falcon
- Microsoft Defender for Endpoint
- Tanium
- Palo Alto Networks
- Cloudflare Zero Trust
- Zscaler ZIA
Full connector list on request. All product names are trademarks of their owners.
Standards
Frameworks we help you meet
| NIST SP 800-207 | Zero Trust Architecture |
|---|---|
| CISA ZTMM | Maturity model mapping |
Questions teams ask
Is every pillar fully automated?
No. We report maturity from live connector signal pillar by pillar, and we are clear where evaluators are still expanding.
Do you install agents?
No. Read-only API connections only.
See what CoreGuardian finds in your environment.
Read-only. No agents. Nothing to rip out.
Request a demo