Continuous Compliance & ATO
Your audit evidence, produced by your security data
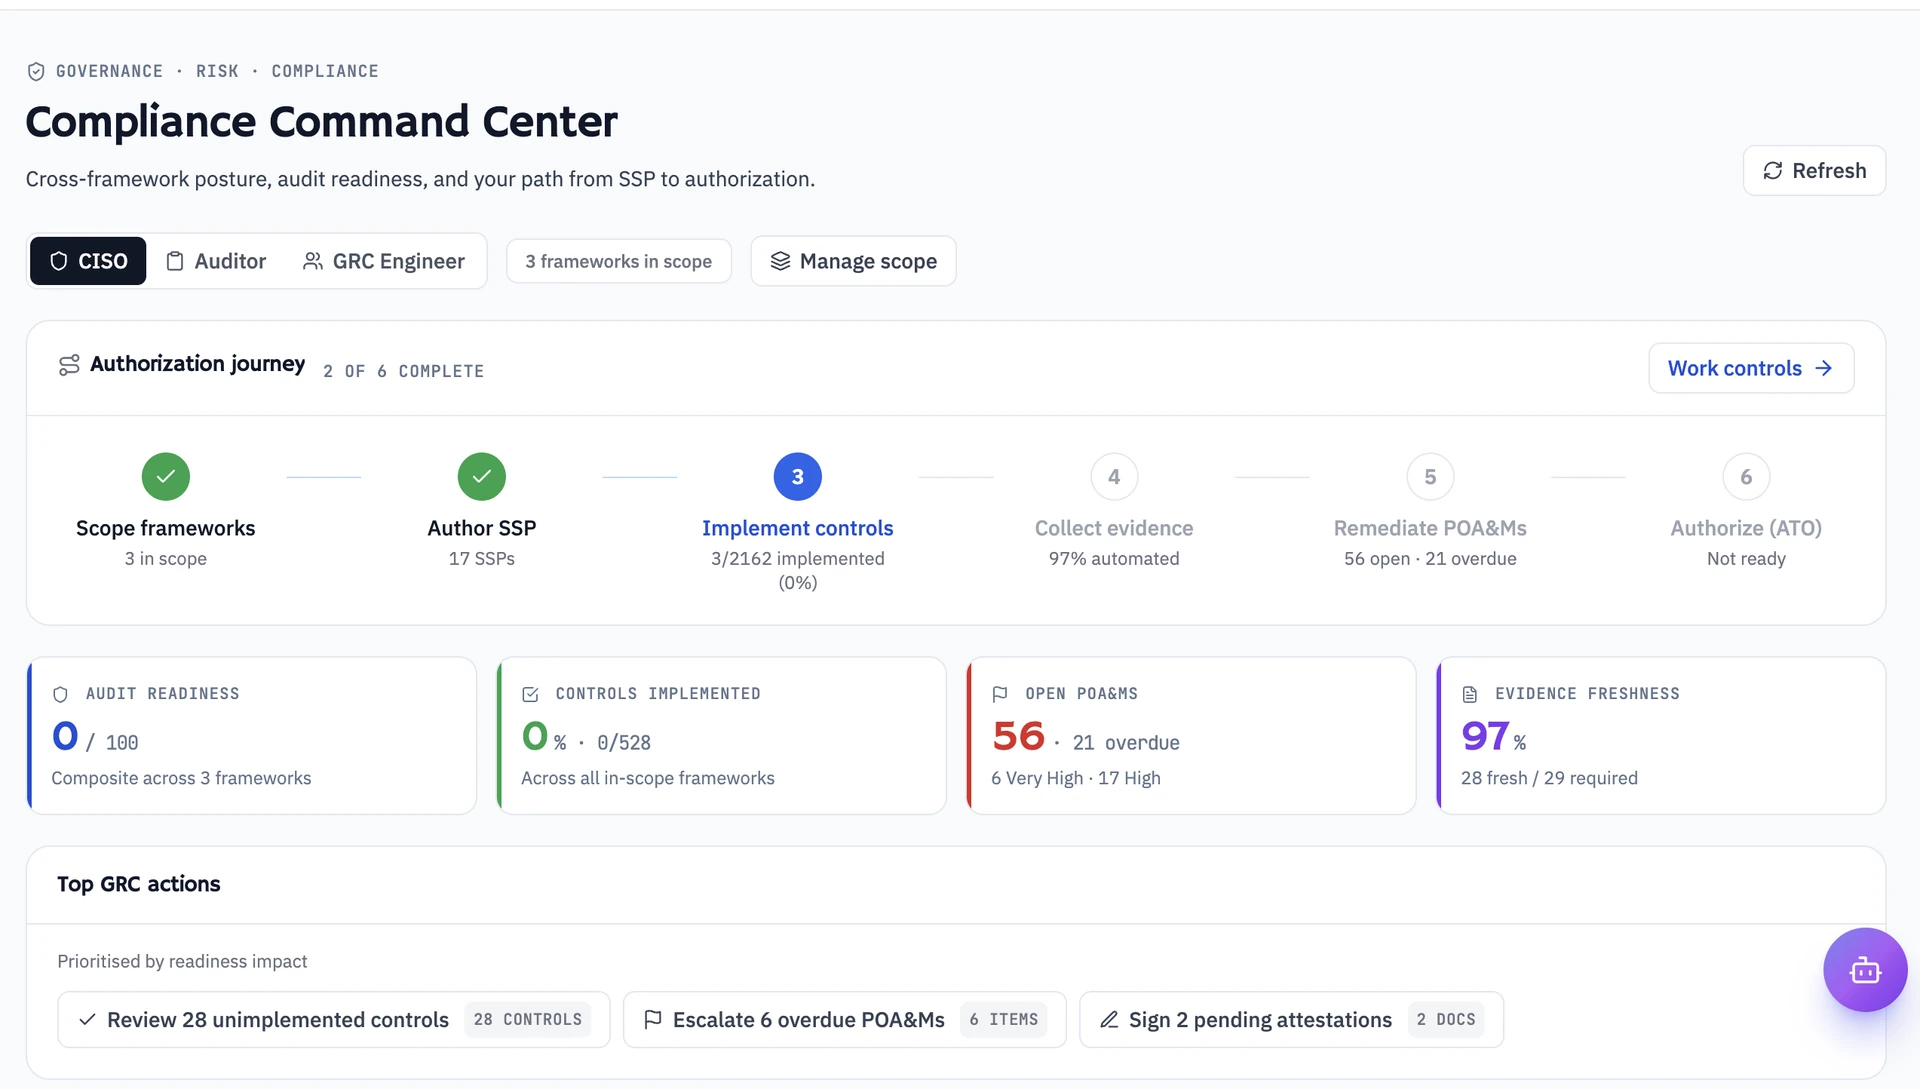
Twelve frameworks, OSCAL exports, POA&M, and ATO state — with assertions owned by your team, never the vendor.
12 frameworks
Seeded catalogs with cross-framework mapping.
OSCAL-native
SSP, POA&M, SAP and SAR exports.
RMF lifecycle
ATO state your ISSO can track.
You assert
Who asserted a control? Always someone on your team.
01
Evidence as a by-product of security work
- Control status tied to live connector signal
- POA&M items with owners and milestones
- Tamper-evident evidence locker
02
Authorizations without a separate evidence project
- SSP authoring with Word/PDF/OSCAL export
- Examiner sessions that are time-boxed
- FedRAMP 20x KSI tracking and SCN support
Connects to
Works with the stack you already own
- Microsoft Entra ID
- Okta
- Google Workspace
- SailPoint
- Ping Identity
- AWS
- Microsoft Azure
- Google Cloud
- Wiz
- CrowdStrike Falcon
- Microsoft Defender for Endpoint
- Tanium
- Tenable Vulnerability Management
- Qualys
Full connector list on request. All product names are trademarks of their owners.
Standards
Frameworks we help you meet
| NIST SP 800-53 Rev 5 | Control catalog foundation |
|---|---|
| OSCAL | Machine-readable SSP and POA&M |
| FedRAMP | Baselines and 20x KSI tracking |
Questions teams ask
Does CoreGuardian hold a FedRAMP authorization?
No. We help you pursue authorization with evidence from your own environment. We make no authorization claim for CoreGuardian itself.
Do you replace our GRC tool?
We complete it — continuous evidence from security data, not another spreadsheet project.
See what CoreGuardian finds in your environment.
Read-only. No agents. Nothing to rip out.
Request a demo