AI Agent Governance
Every AI agent in your enterprise, inventoried and governed
Discovery across major AI providers, with policy controls and human-in-the-loop approvals — so agents are visible before they become shadow IT.
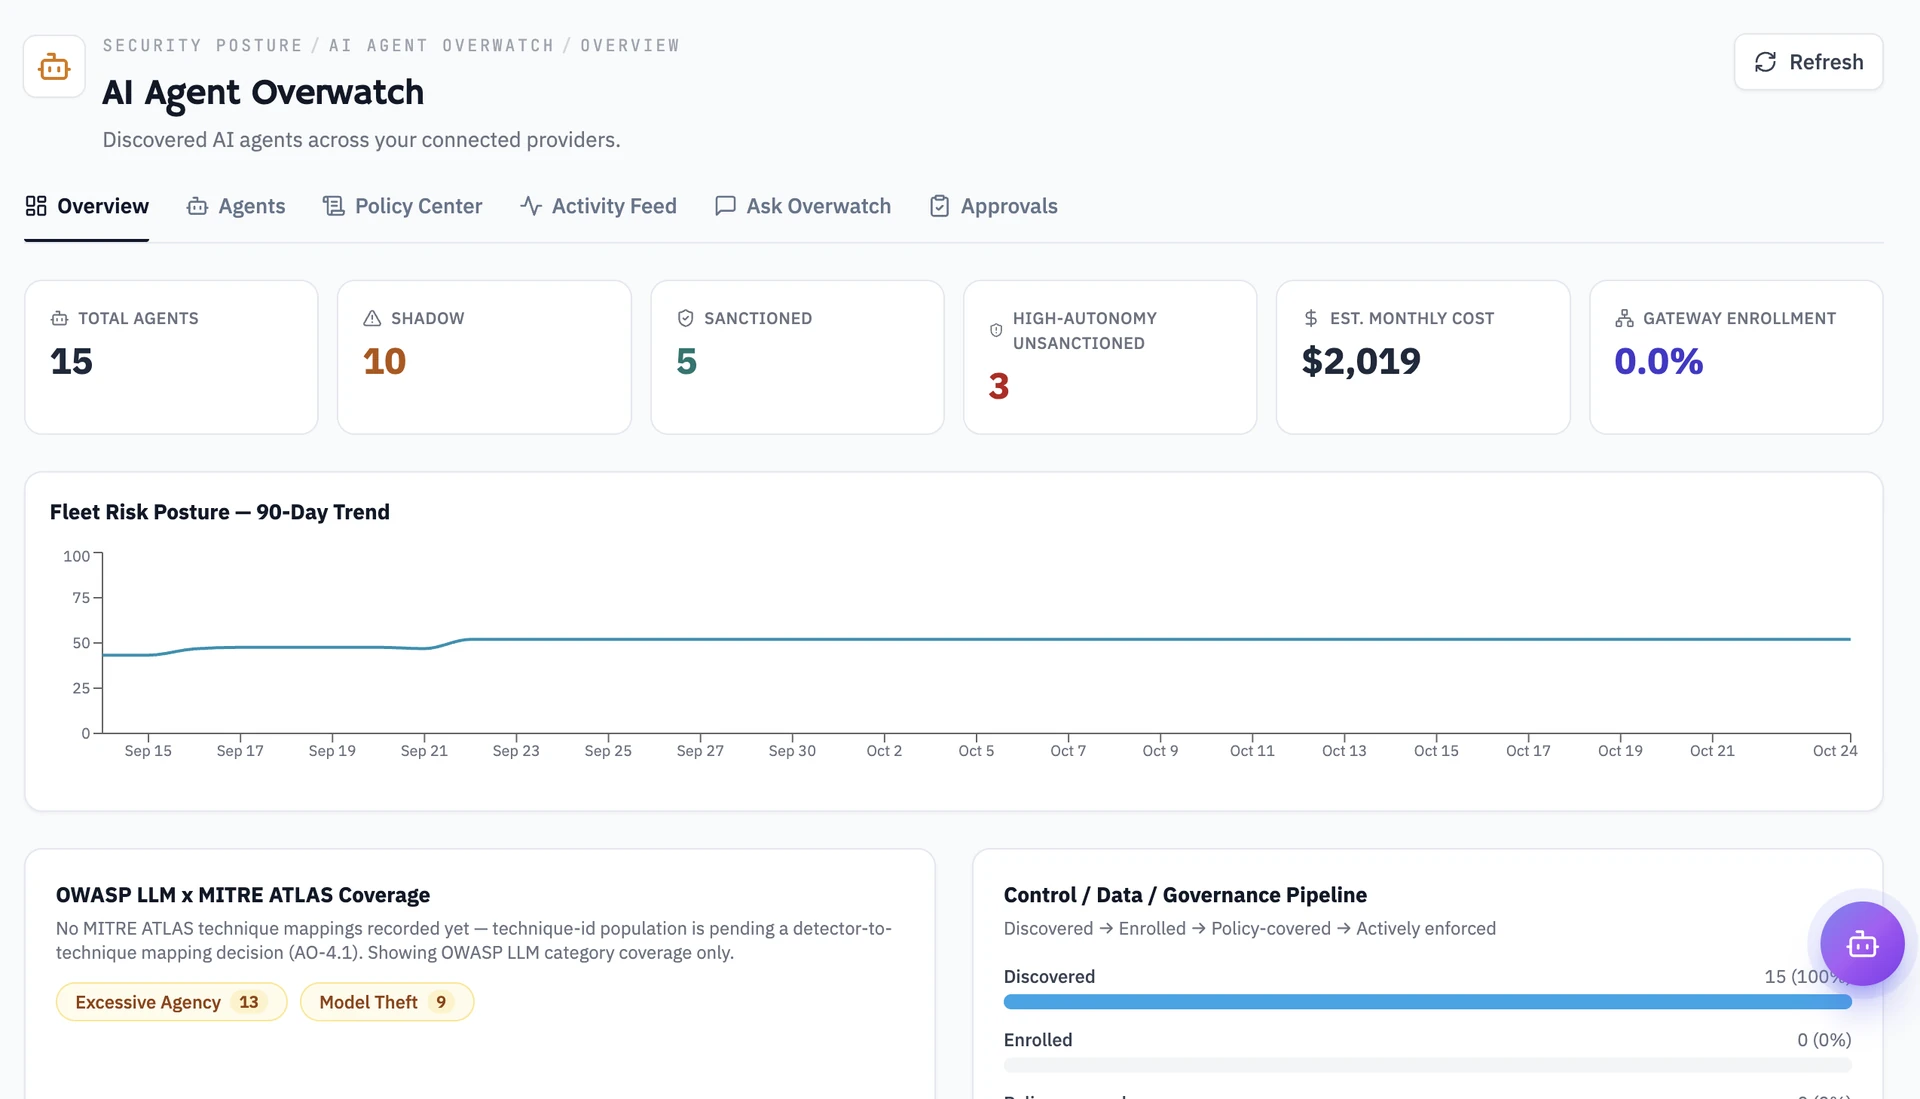
Inventory
Agents across Anthropic, OpenAI, Bedrock, Vertex, Azure OpenAI, Copilot.
Policy gateway
Allow, block, kill session, require approval, redact.
Approvals
Human-in-the-loop when the policy says so.
Activity
A feed your security team can actually read.
01
See the agents before they become a surprise
- Provider inventory in one place
- Risk model for agent posture
- Works alongside the tools you already approved
02
Govern with policy, not hope
- Gateway actions your security team defines
- Approvals when humans must decide
- Mapped to AI governance workflows you already run
Connects to
Works with the stack you already own
- Microsoft Entra ID
- Okta
- Google Workspace
- SailPoint
- Ping Identity
- AWS
- Microsoft Azure
- Google Cloud
- Wiz
- Anthropic
- OpenAI
- Microsoft 365 Copilot
Full connector list on request. All product names are trademarks of their owners.
Standards
Frameworks we help you meet
| NIST AI RMF | AI system inventory mapping |
|---|---|
| EU AI Act | Workflow support for classification work |
Questions teams ask
Is this an AI that runs your security program?
No. This page is about governing AI agents in your enterprise — inventory and policy, not replacing your analysts.
Do you install agents on endpoints?
No. Read-only connections to the AI providers and gateways you already use.
See what CoreGuardian finds in your environment.
Read-only. No agents. Nothing to rip out.
Request a demo