Federal & Defense

Continuous monitoring that stands up in front of an AO.

The RMF lifecycle, OSCAL SSP and POA&M, and ATO state, fed by verified control data instead of spreadsheets.
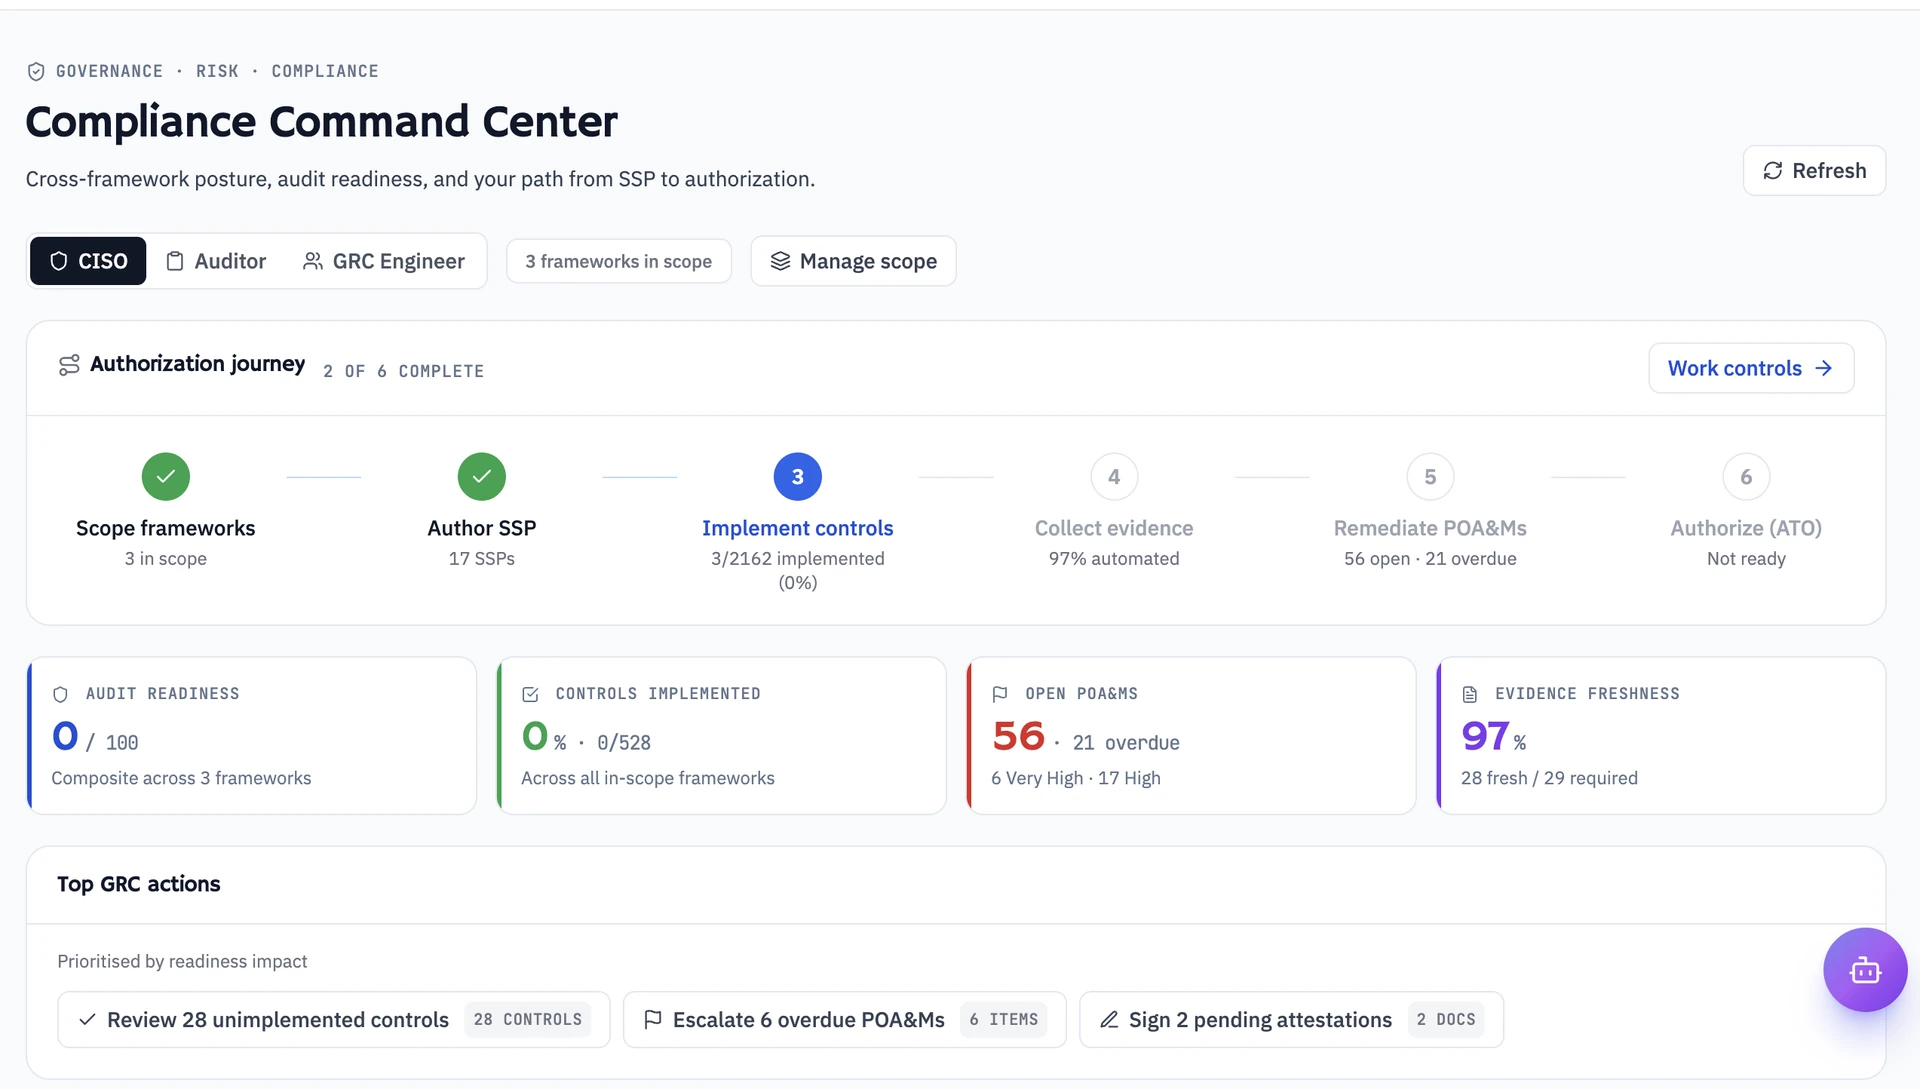
Compliance Command Center
Compliance Command Center with authorization journey, audit readiness, and open POA&Ms

The ISSO day

Less assembling. More assessing.

Before

Evidence is a project.

  • Screenshots and exports gathered by hand before every assessment.
  • The SSP drifts from reality the day after it is signed.
  • POA&M lives in a spreadsheet nobody trusts.
  • Continuous monitoring is a monthly report.
With CoreGuardian

Evidence is a by-product.

  • Control state verified from connected tools, with provenance.
  • SSP authored in-platform and exported to OSCAL, Word or PDF.
  • POA&M items opened from findings, each with an owner.
  • Drift surfaces the day it happens.

RMF lifecycle

All seven steps, one record.

NIST SP 800-37 Rev 2, with ATO state tracked as a state machine rather than a document date.
  1. 01Prepare
  2. 02Categorize
  3. 03Select
  4. 04Implement
  5. 05Assess
  6. 06Authorize
  7. 07Monitor ยท continuous
01

OSCAL-native documentation.

  • SSP, POA&M, SAP, SAR and component definitions in OSCAL.
  • SSP export to Word and PDF for reviewers who want paper.
  • Catalog updates never change your baseline without your review.
Compliance Command Center
Authorization journey from scoped frameworks through SSP to ATO with open POA&Ms
02

Evidence an assessor can check.

  • Tamper-evident evidence locker an assessor can verify.
  • Time-boxed examiner sessions by magic link.
  • Attestations attributed to named roles on your team.
Compliance Command Center
Audit readiness, evidence freshness, and GRC actions ranked by readiness impact
03

Zero Trust and quantum mandates.

  • CISA ZTMM self-assessment export (Word, JSON, OSCAL POA&M) for M-22-09 reporting.
  • Crypto inventory, HNDL exposure window and CNSA 2.0 alignment view.
  • CMMC Level 2 and Level 3 control catalogs.
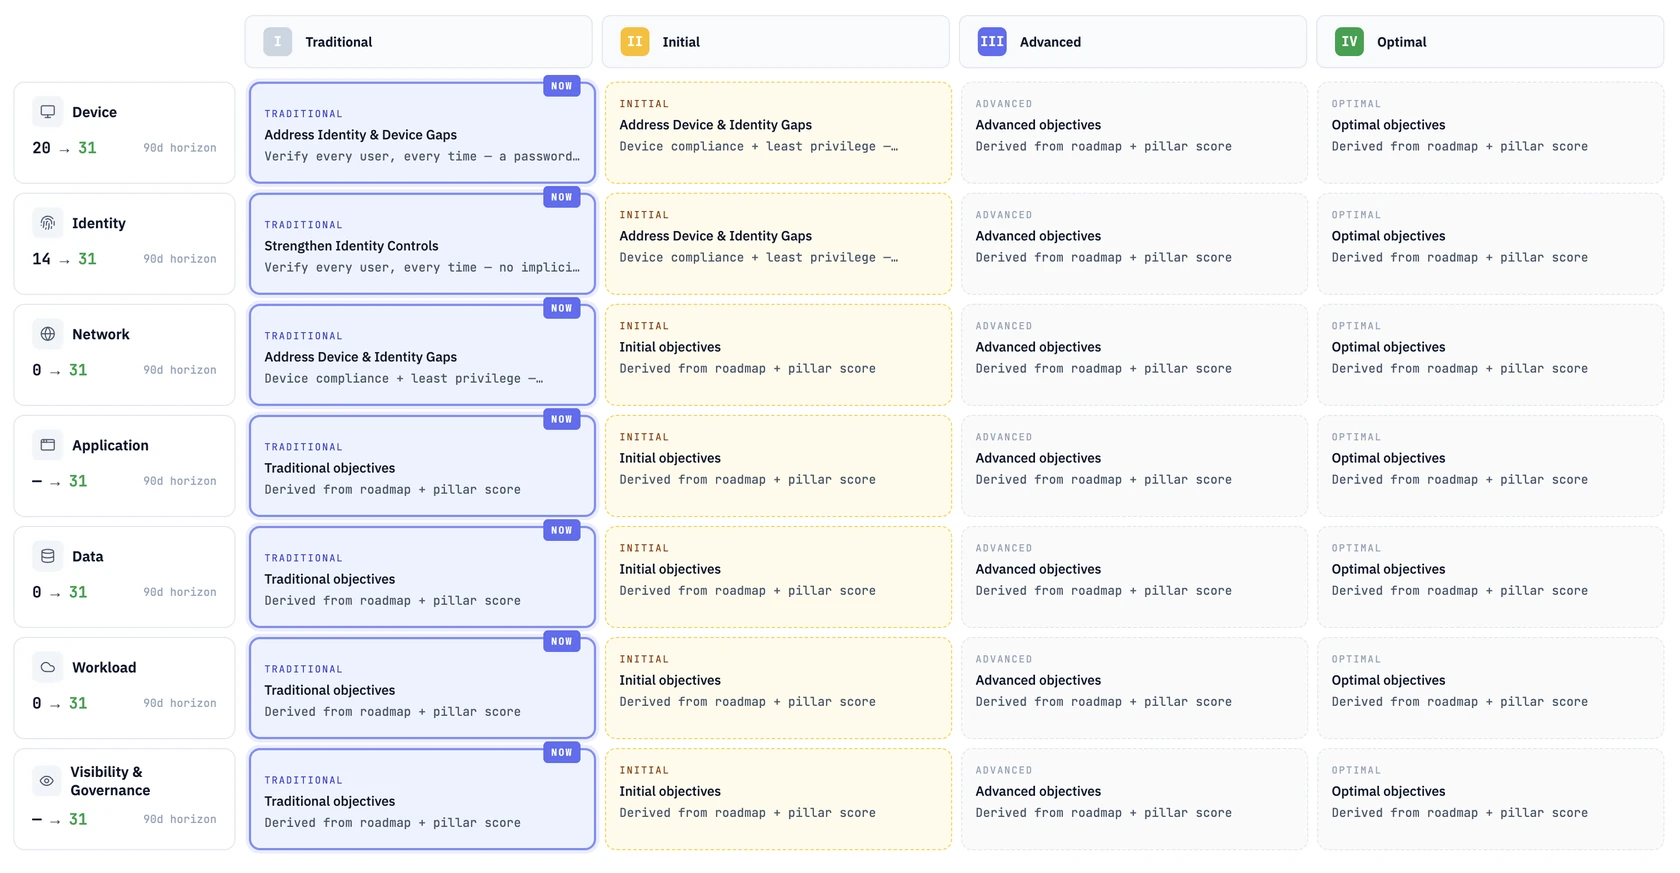
Zero Trust
Zero Trust maturity matrix across CISA ZTMM stages with current pillar posture
The attribution ruleWho asserted AC-2 is implemented? Always a person on your team, never the vendor.

The platform owns the catalog. You own your assertions.

Accessibility

Section 508

We design and test against WCAG 2.1 AA. A VPAT will be published when it is complete.

Bring your next assessment forward.

Read-only. No agents. Nothing to rip out.

Request a demo