Identity & NHI Security
Every identity, human and non-human, with the keys it holds
People, service accounts, and secrets in one place — with risk that reflects privilege, MFA posture, and credential age.
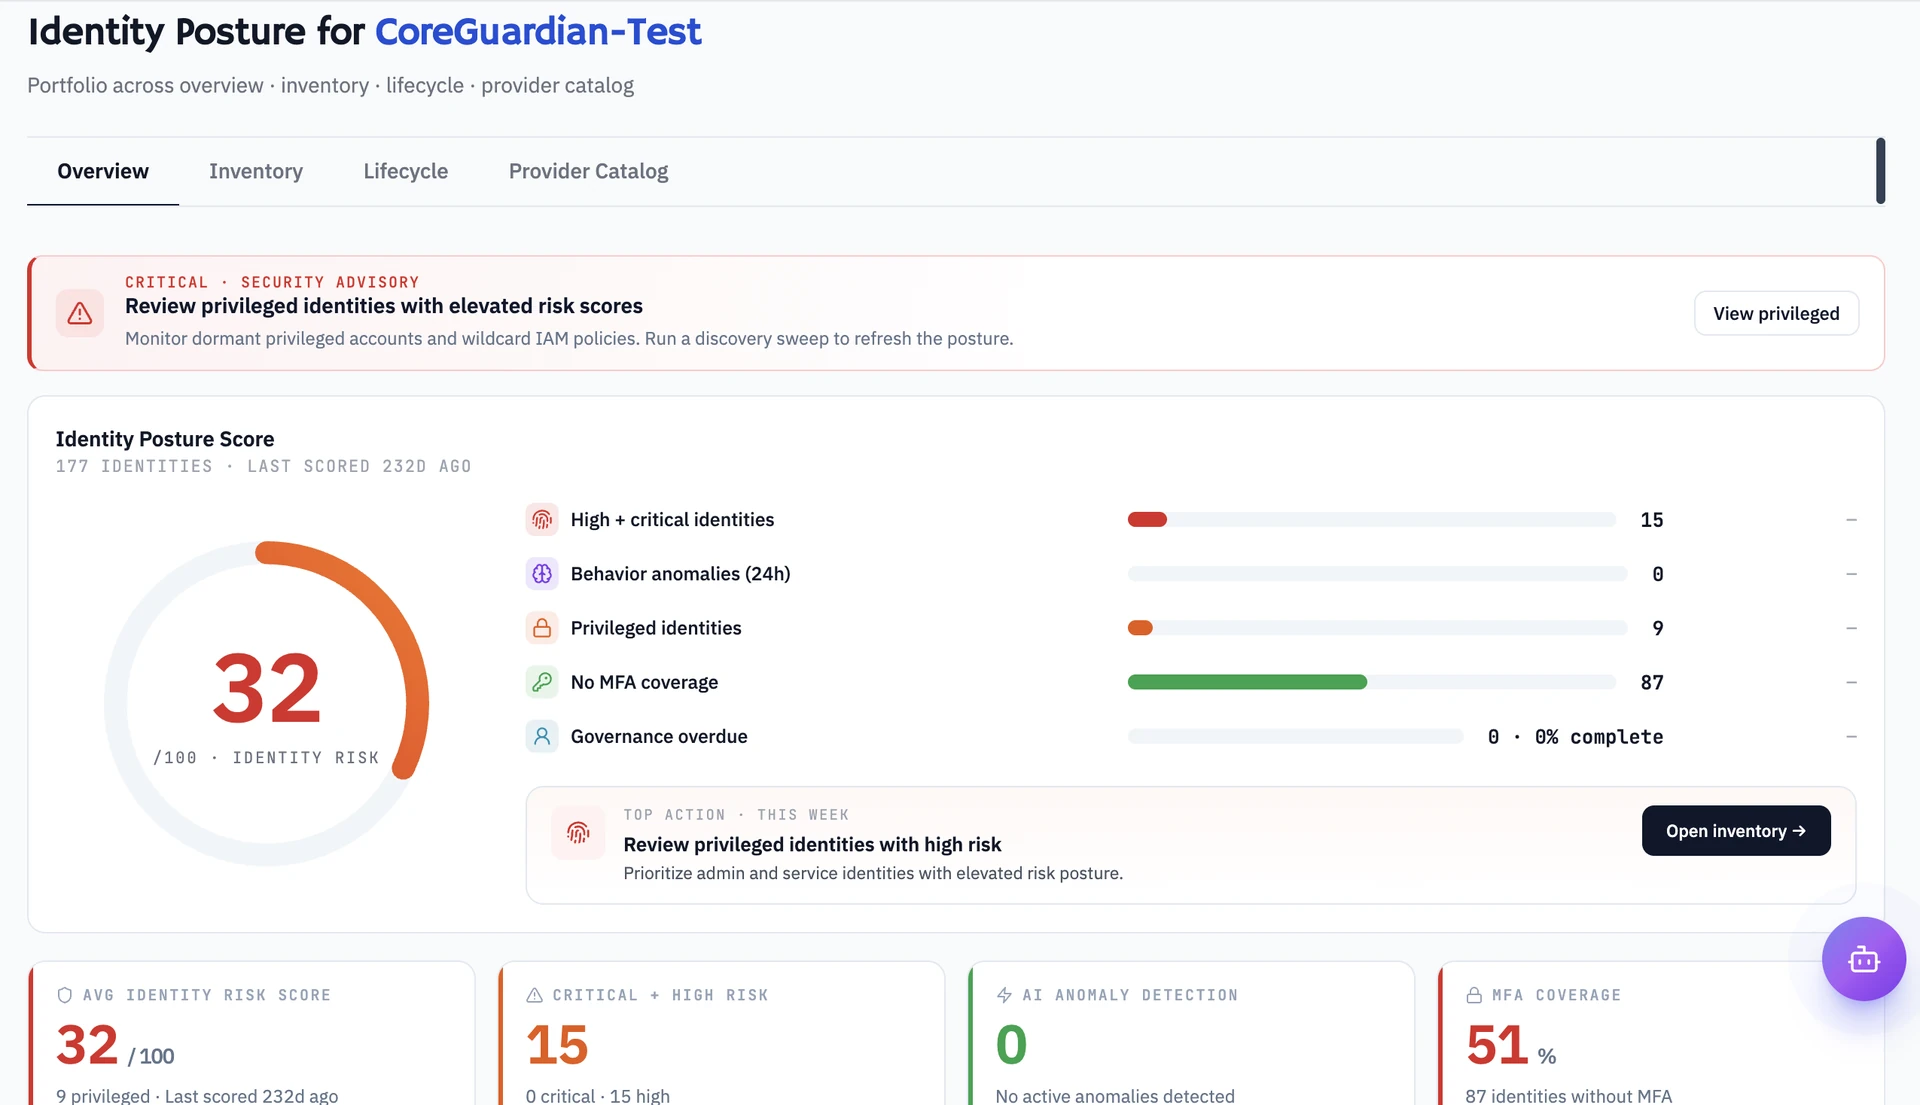
People + NHI
Unified inventory across major identity providers and cloud sources.
Privilege & MFA
Identity risk that reflects how an account can actually be used.
Secrets & Keys
Credential age, algorithm, and ownership in one view.
Contradictions
Terminated in HR, still active in the IdP — surfaced as a finding.
01
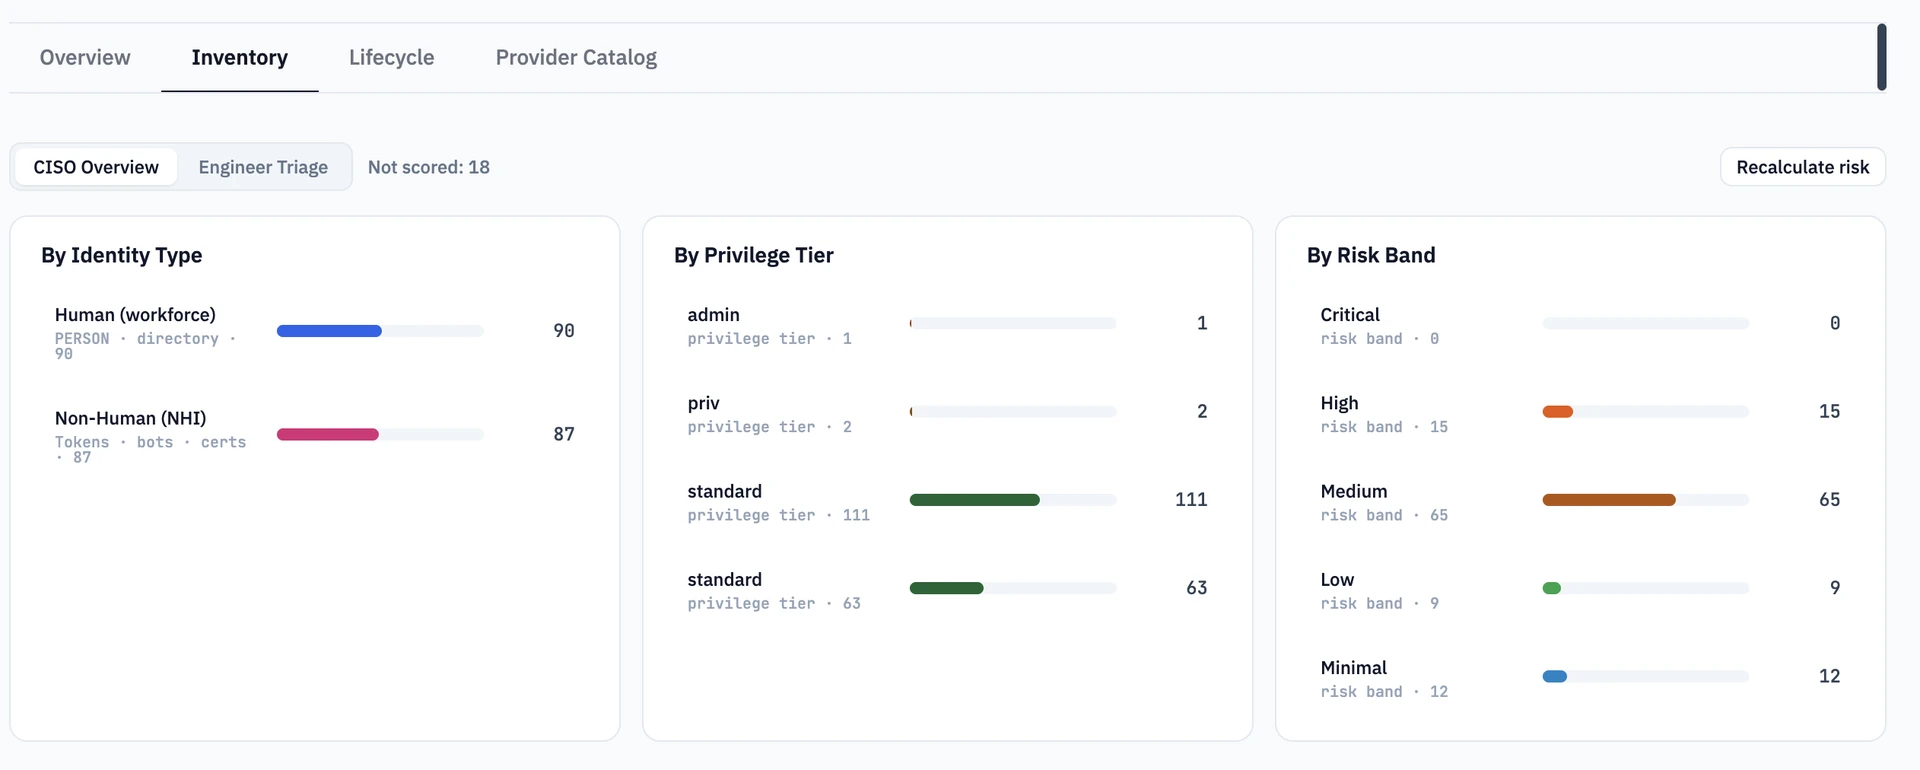
One inventory of human and non-human identities
- Directory, cloud IAM, and code-adjacent identities
- Service accounts treated as first-class
- Owners and reach visible together
02
Risk that reflects privilege, not just presence
- Admin without MFA rises
- Stale privileged accounts called out
- Cross-tool contradictions become findings
Connects to
Works with the stack you already own
- Microsoft Entra ID
- Okta
- Google Workspace
- SailPoint
- Ping Identity
- AWS
- Microsoft Azure
- Google Cloud
- Wiz
- GitHub
- ServiceNow
Full connector list on request. All product names are trademarks of their owners.
Standards
Frameworks we help you meet
| NIST SP 800-53 | AC and IA control families |
|---|---|
| CISA ZTMM | Identity pillar maturity from live signal |
Questions teams ask
Do you install agents?
No. Read-only API connections only.
Do you replace our IdP?
No. We complete it — one picture across the identity tools you already run.
Where is my data hosted?
On Google Cloud in the United States. Details are on our Trust page.
See what CoreGuardian finds in your environment.
Read-only. No agents. Nothing to rip out.
Request a demo