Exposure & Risk Prioritization
A short list, ranked by what the business stands to lose
One reconciled inventory across the tools you already run. Findings that matter rise because of business context, exposure, and live exploitation — not a raw CVSS sort.
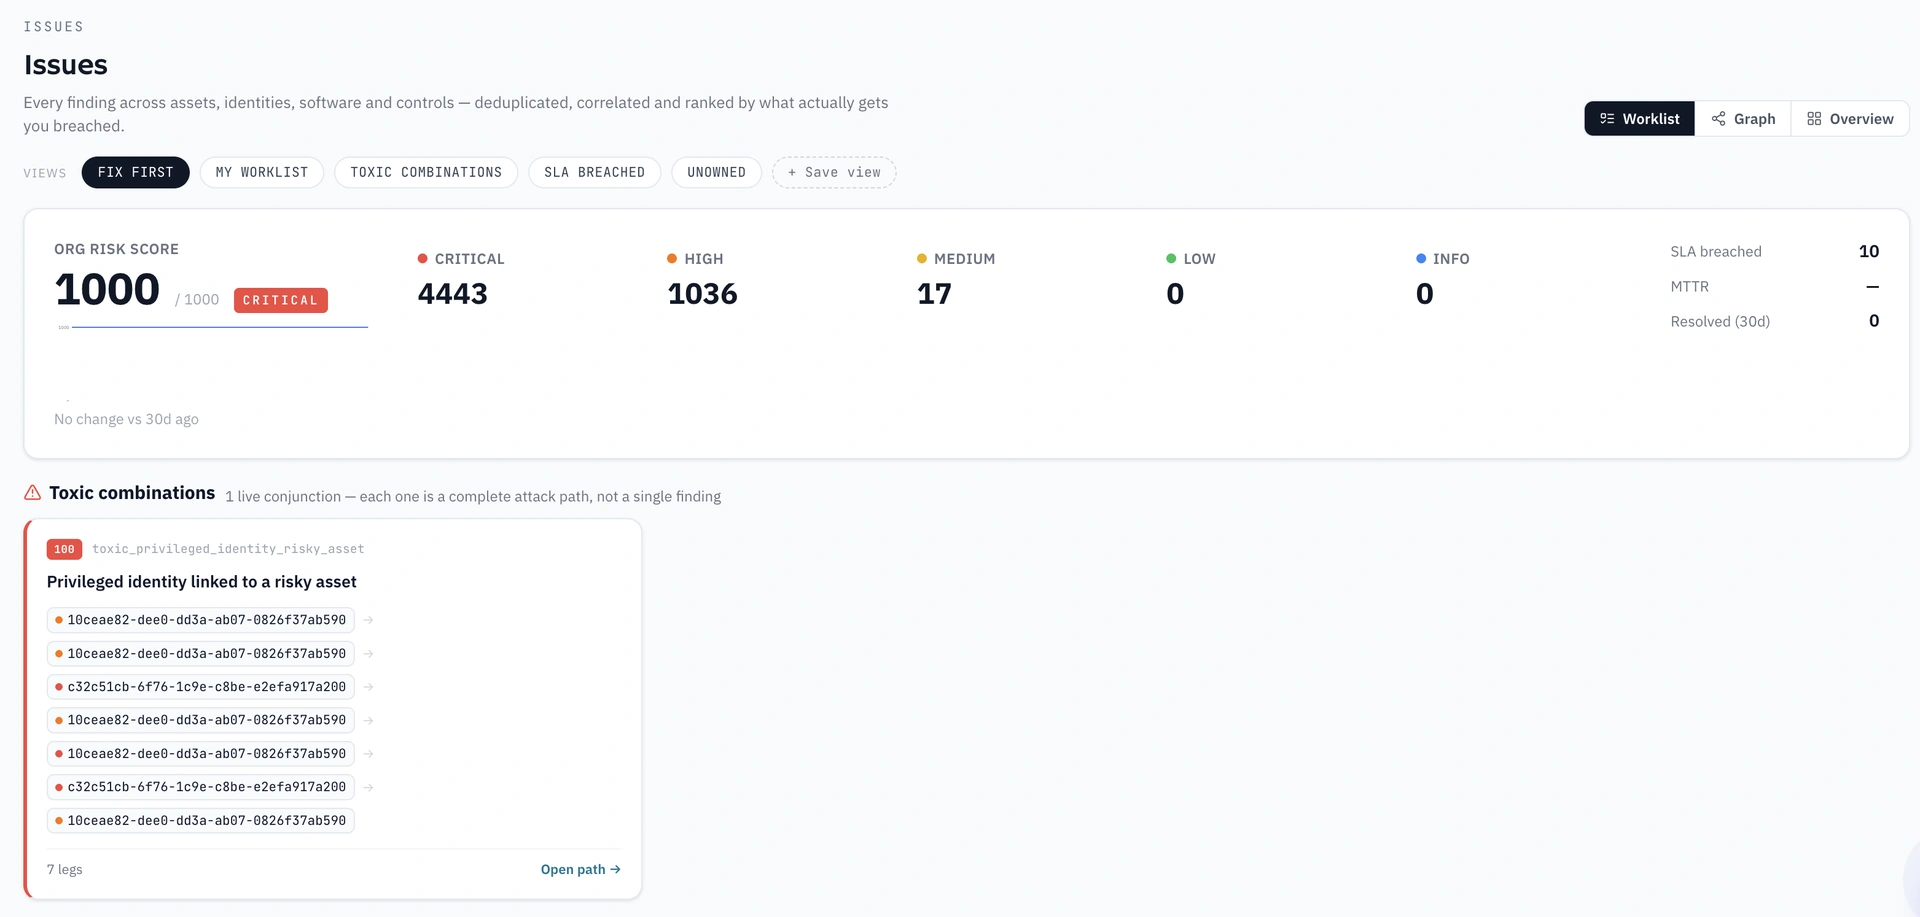
One inventory
Assets and identities reconciled across connectors into a single record.
Business context
Criticality, exposure, and identity reach change the order of work.
Live exploitation
KEV, EPSS and related feeds inform what needs attention today.
Owned issues
Toxic combinations and choke points land with an owner, not a ticket pile.
See the same asset the way every tool sees it
- Golden-record inventory across identity, endpoint, cloud and scanners
- Contradictions between tools surface as findings
- Scanless CVE matching from software inventory
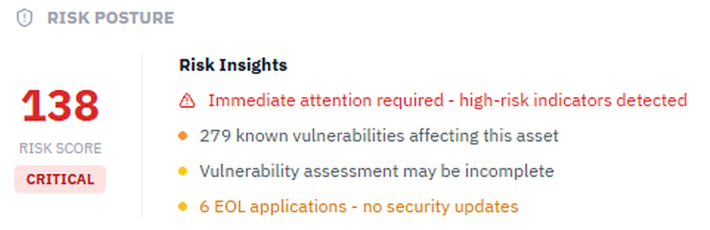
Rank by business risk, not CVSS alone
- Business context and exposure reshape priority
- Active exploitation signals raise the handful that matter
- Same CVE, different assets — different urgency
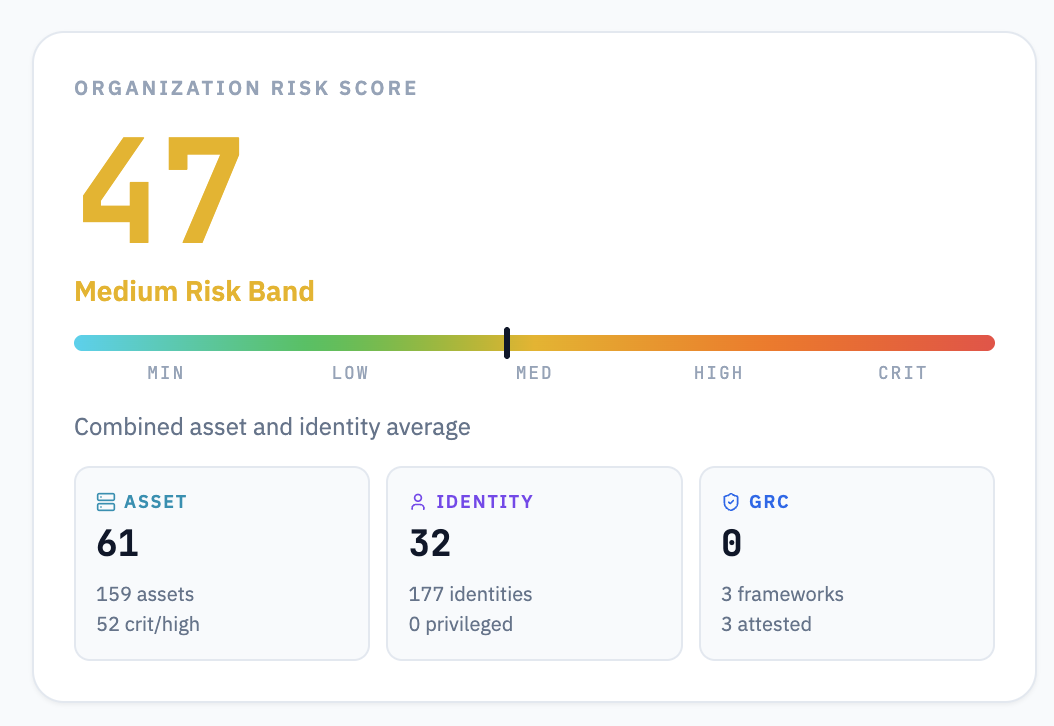
Issues with owners, not another dashboard
- Correlated org-level issues
- Toxic combinations and choke points
- Worklists your team can close
Connects to
Works with the stack you already own
- Microsoft Entra ID
- Okta
- Google Workspace
- SailPoint
- Ping Identity
- AWS
- Microsoft Azure
- Google Cloud
- Wiz
- CrowdStrike Falcon
- Microsoft Defender for Endpoint
- Tanium
- Tenable Vulnerability Management
- Qualys
Full connector list on request. All product names are trademarks of their owners.
Standards
Frameworks we help you meet
| CISA KEV | Known exploited vulnerabilities in the ranking context |
|---|---|
| FIRST EPSS | Exploit probability as one input to priority |
| MITRE ATT&CK | Threat context for analyst workflows |
Questions teams ask
Do you install agents?
No. CoreGuardian connects with read-only API access to tools you already run.
Do you need write access?
No. Connections are read-only by design.
What if two tools disagree?
That disagreement is a finding. We surface it so someone can own it.
Does this replace our scanners?
No. We complete them — one ranked list from the stack you already own.
See what CoreGuardian finds in your environment.
Read-only. No agents. Nothing to rip out.
Request a demo