Your security program assumes your controls work. CoreGuardian™ verifies it continuously. We read the tools you already run, rank the handful of problems that actually put the business at risk, and hand you the audit evidence.
See your organization’s risk.
In one walkthrough, see what matters, who owns it, and what proves it.
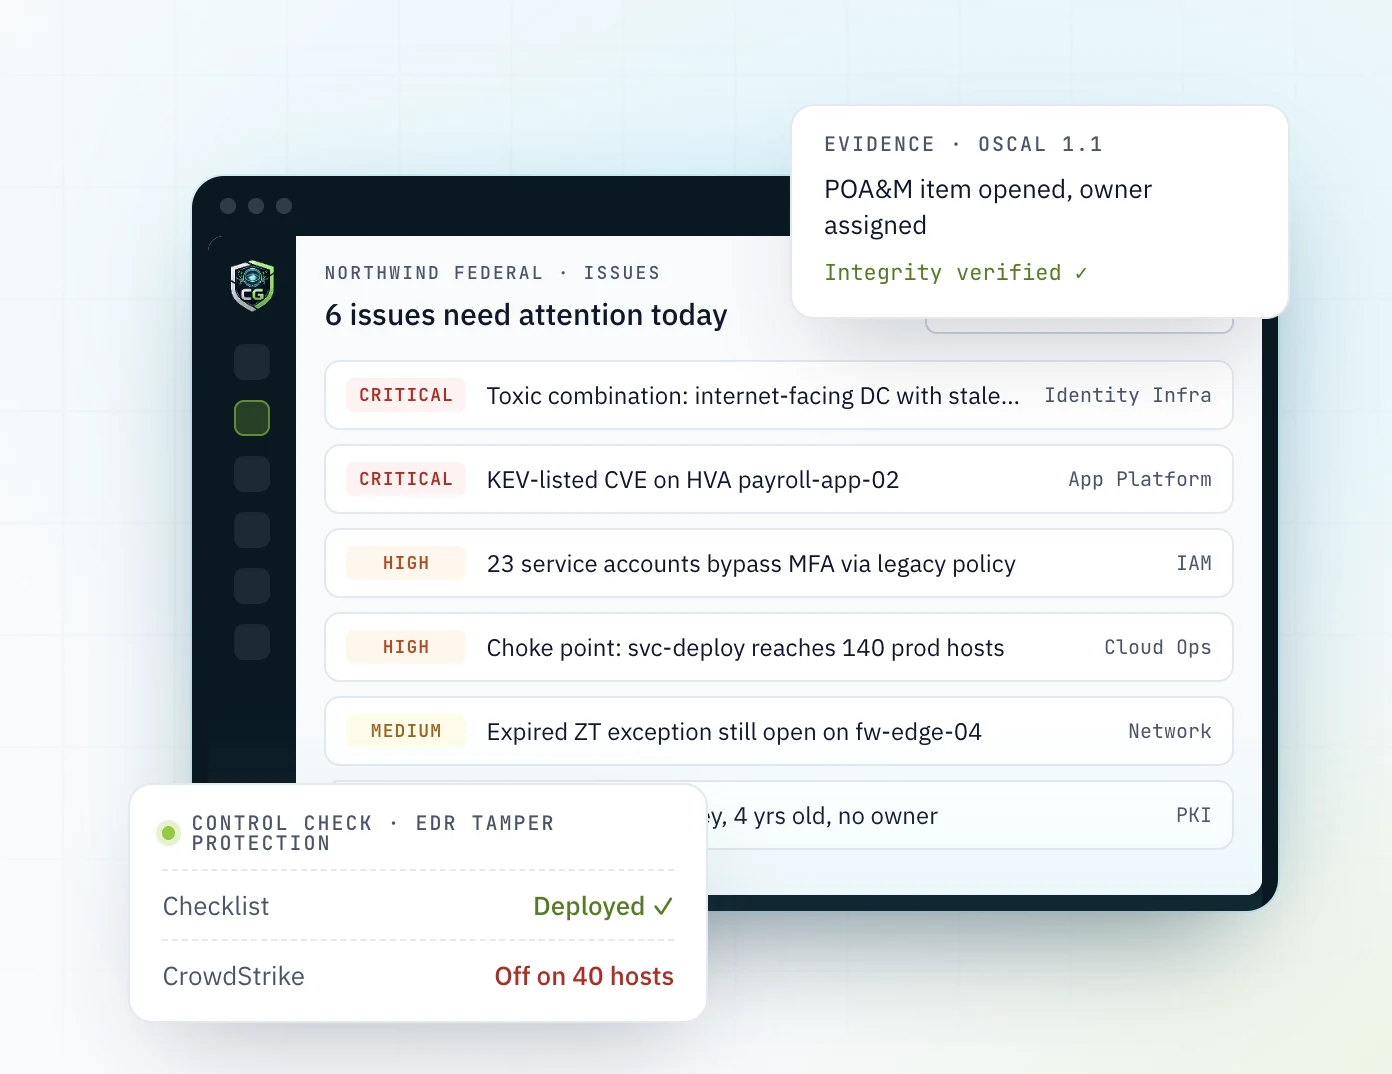
Follow an illustrative scenario from connected signal to a ranked, owned issue tracked to closure (POA&M), then captured as tamper-evident evidence.
Connected workflowSignal → priority → proof
Zero Trust Exposure Management, with GRC built in
One platform. Four jobs.
01 · SeeAssets + identity
What’s here?
36
Laptops running a banned app
02 · CheckZero Trust posture
Is it set up right?
14
Laptops with EDR turned off
03 · FixExposure management
What do we fix first?
10
Ranked and assigned this week
04 · ProveGRC
Can we prove it?
4
Records tied to one fix
Each view works from the same record.
In the product
One laptop. Four tools. One score.
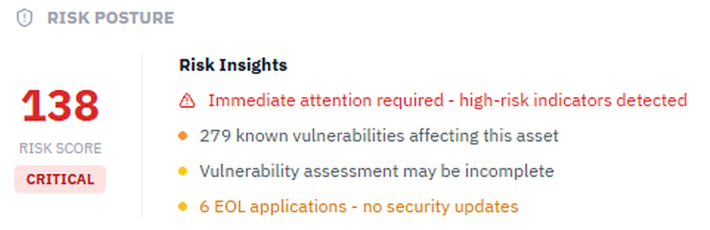
Staff laptopSTAFF-L-2291Device risk138
Identity
Unknown account signed in
Software
279 known vulnerabilities
Scanner
No authenticated scan yet
EDR
All policies applied
Same bug. Two laptops.
CVE-2023-38831 · CVSS 7.8 · Actively exploited
Front-desk laptop
Standard user, no admin rights
Exposure
Office network, filtered
Controls
EDR blocking
CoreGuardian says38Normal patch cycle
IT admin laptop
Domain admin, MFA off
Exposure
Off-site, no secure access
Controls
EDR in detect-only
CoreGuardian says138Fix this week
Context decides the order, not severity alone.
Ranked and owned
First on the list.
Business context, exposure, identity reach and live exploitation point to one gateway.
01
Exposed admin
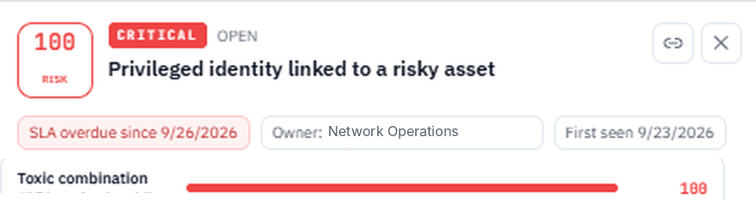
Admin without MFA on the gateway
Owner · Network Operations
100
02
Actively exploited
Exploited CVE on that gateway
100
03
Unknown account
Unknown account on STAFF-L-2291
92
04
Leftover admin
Former contractor still an admin
88
GRC and compliance
The fix is the evidence.
Engineers and auditors work from one record.
Item 1 closed · Admin turns on MFA
1
Control
One check, every framework in scope
2
Status
Partially implemented → Implemented
3
Gap list
Gap closed, owner and date recorded
4
Evidence
Tamper-evident proof from the identity signal
The loop follows one connected record from signal through business-context ranking, ownership, closure and tamper-evident evidence.
What nobody is checking
Deployed isn’t the same as working.
GRC checks that a control was deployed. The SOC watches what fires. Engineering knows what it built. Nobody checks, continuously, that the control is still running, still configured correctly, and still doing its job.
That gap is where risk actually lives. It is also why the board question takes two weeks to answer.
Product workflow
From disconnected data to proof your controls are improving.
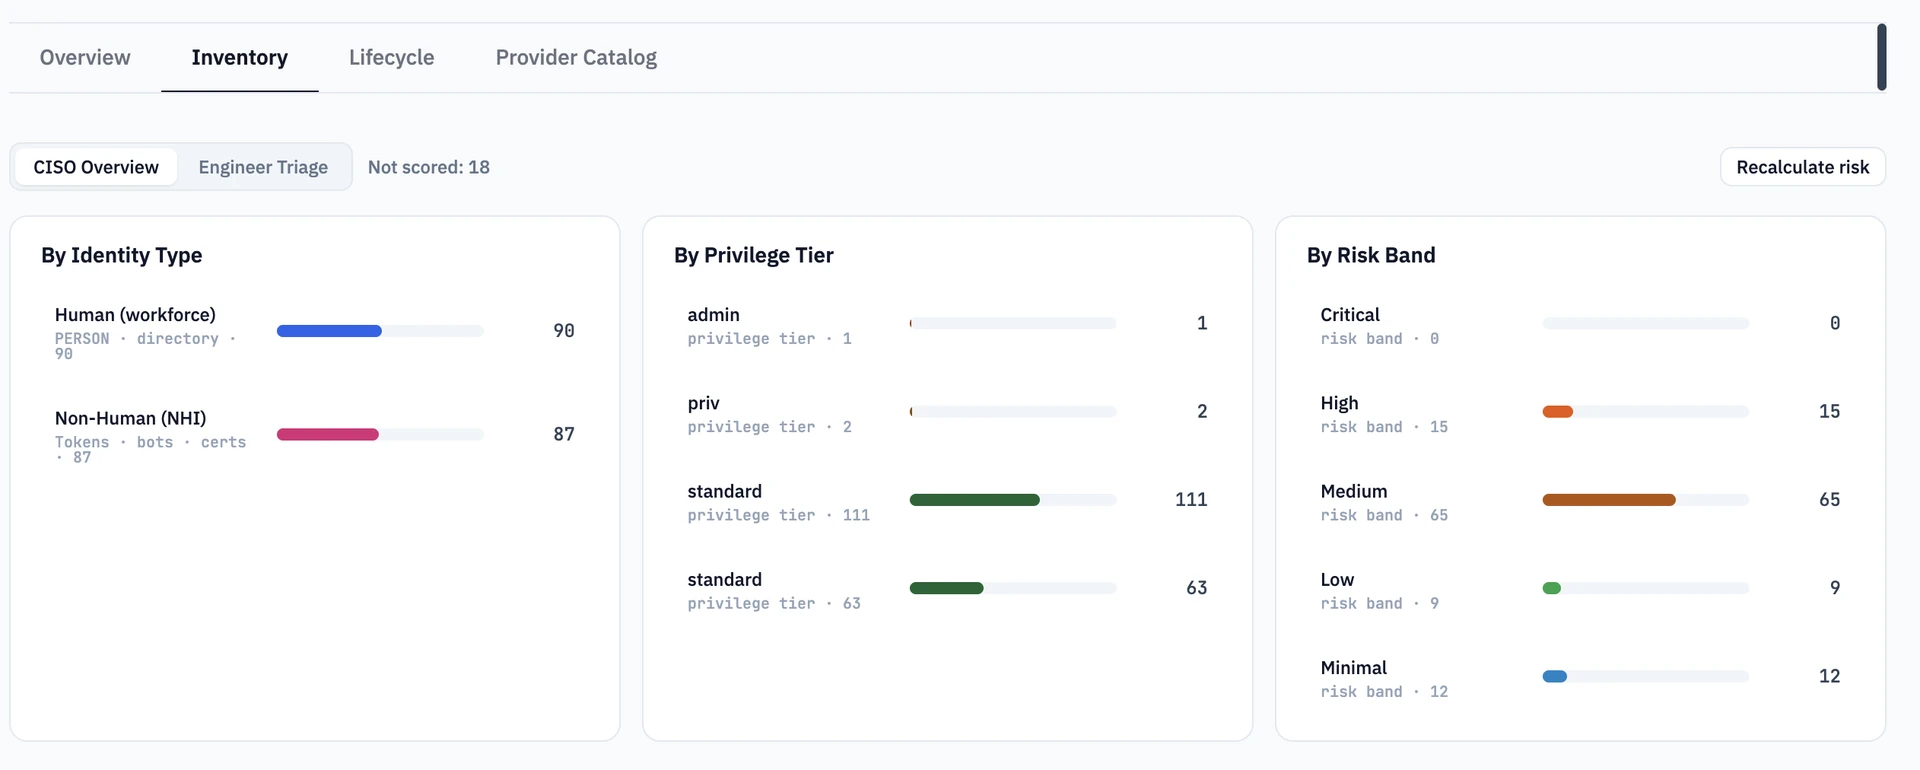
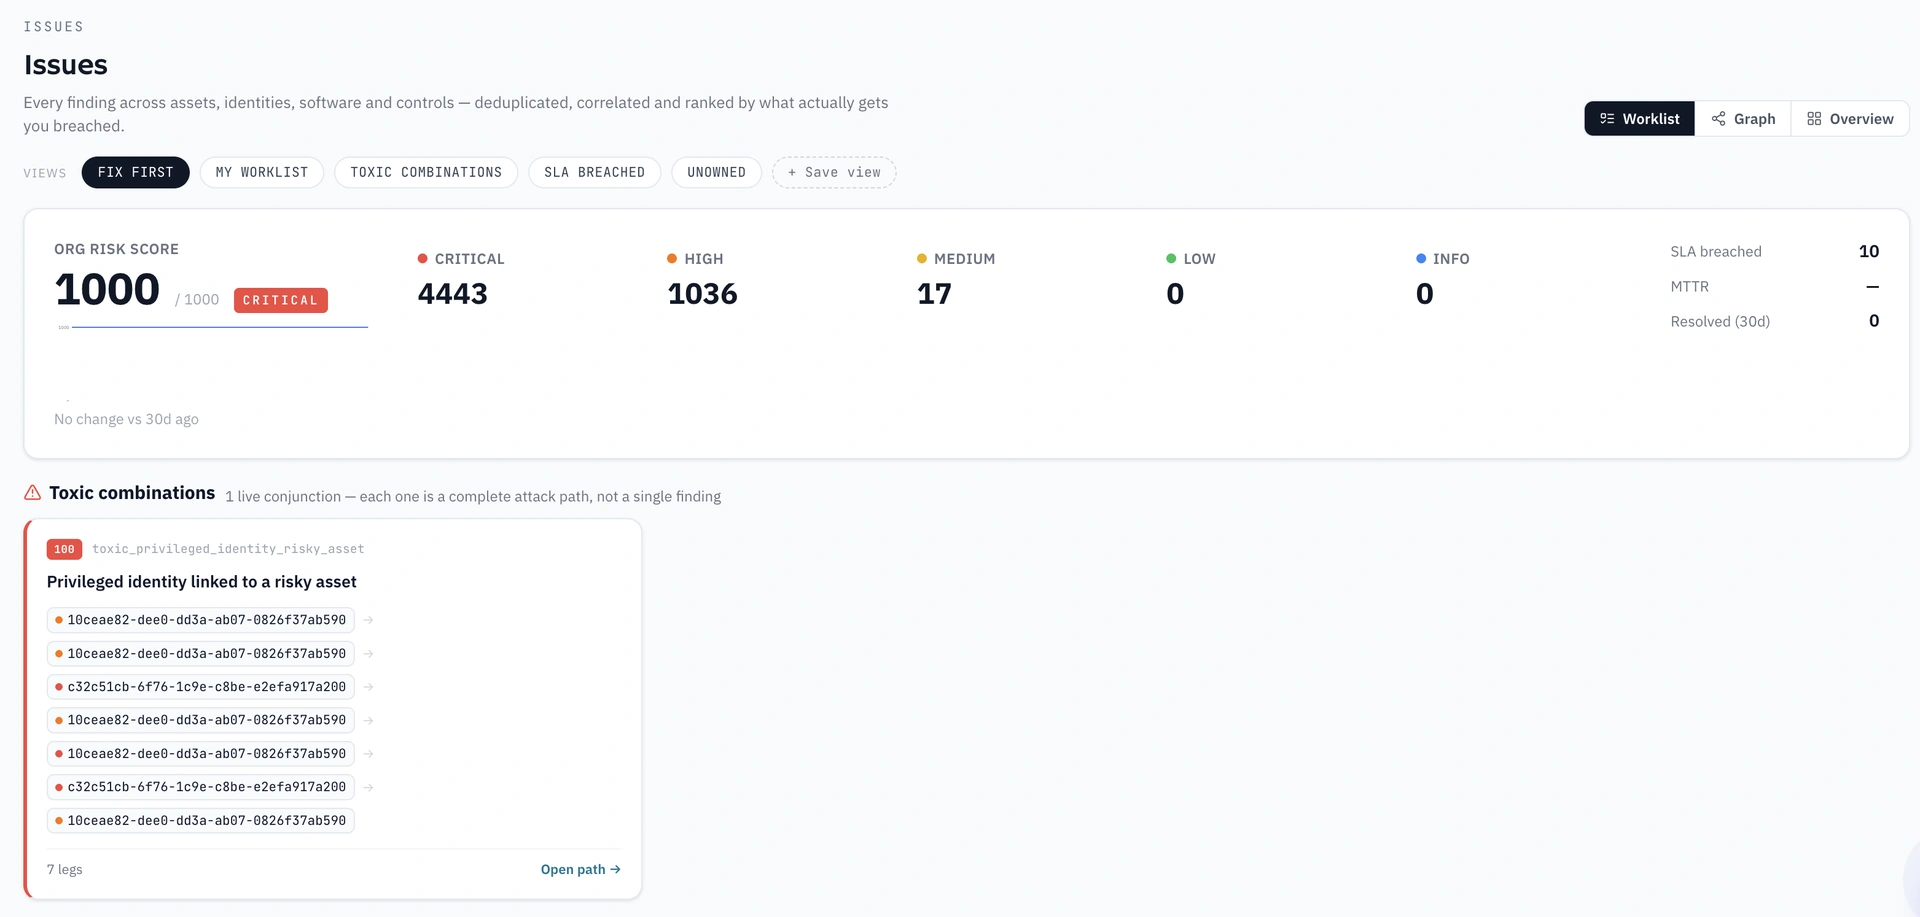
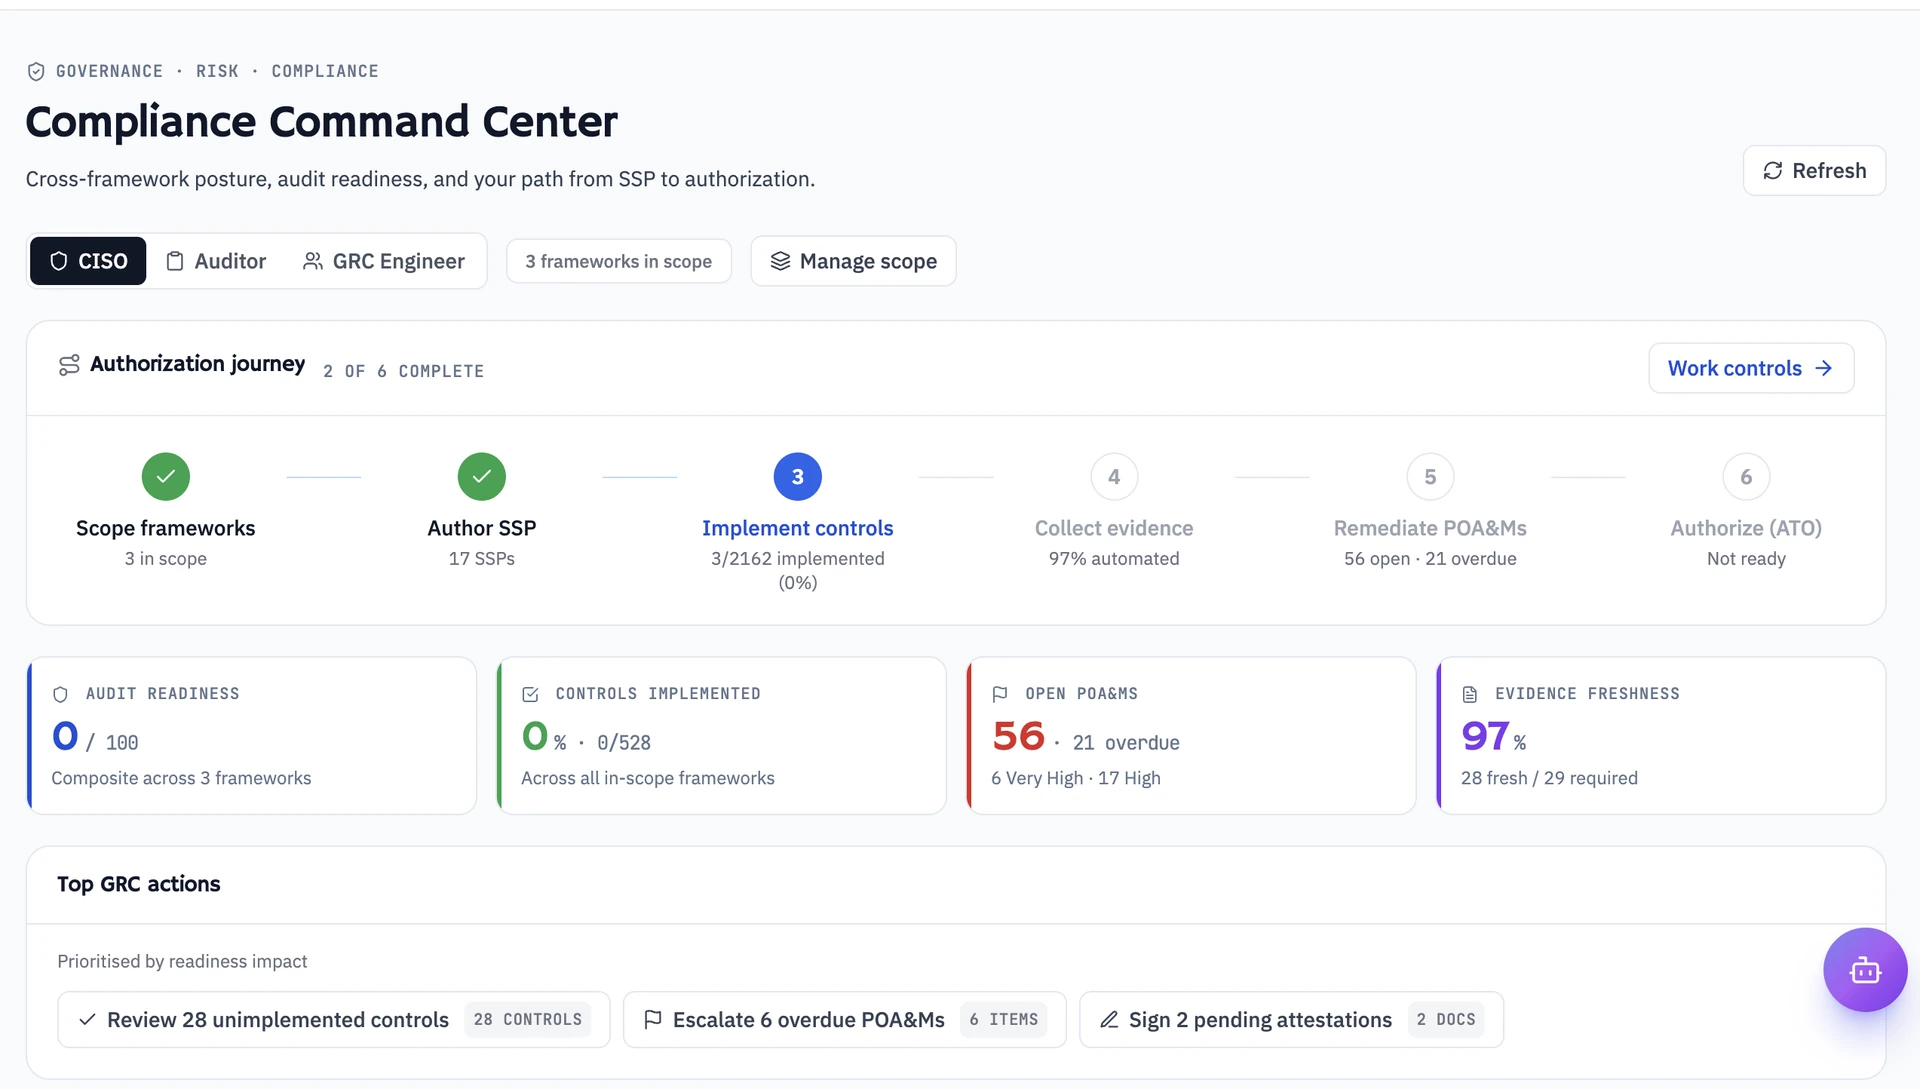
CoreGuardian connects structured security records, ranks what matters, guides owned remediation, and turns the work into evidence.
Inventory
Issue detail
Risk posture
Issues worklist
Compliance Command Center
01 · Structured signal
Collect
Maintain structured security information from existing tools.
Assets
Software
Identities
Configurations
Vulnerabilities
02 · The Trace
Connect & Enrich
Normalize, reconcile, connect relationships, and enrich findings with CVE and threat context.
Normalize and clean
Reconcile duplicates
Connect relationships
Enrich with CVE and threat context
Surface conflicts and gaps
03 · Business context
Prioritize
Correlate business importance, exposure, vulnerabilities, identity context, and threat intelligence.
Asset importance
Internet exposure
Vulnerability context
Identity reach
Threat intelligence
04 · Owned work
Improve
Guide remediation, identify owners, track issues, and verify control status where signal exists.
Remediation guidance
Issue ownership
Tracked to closure
Control verification
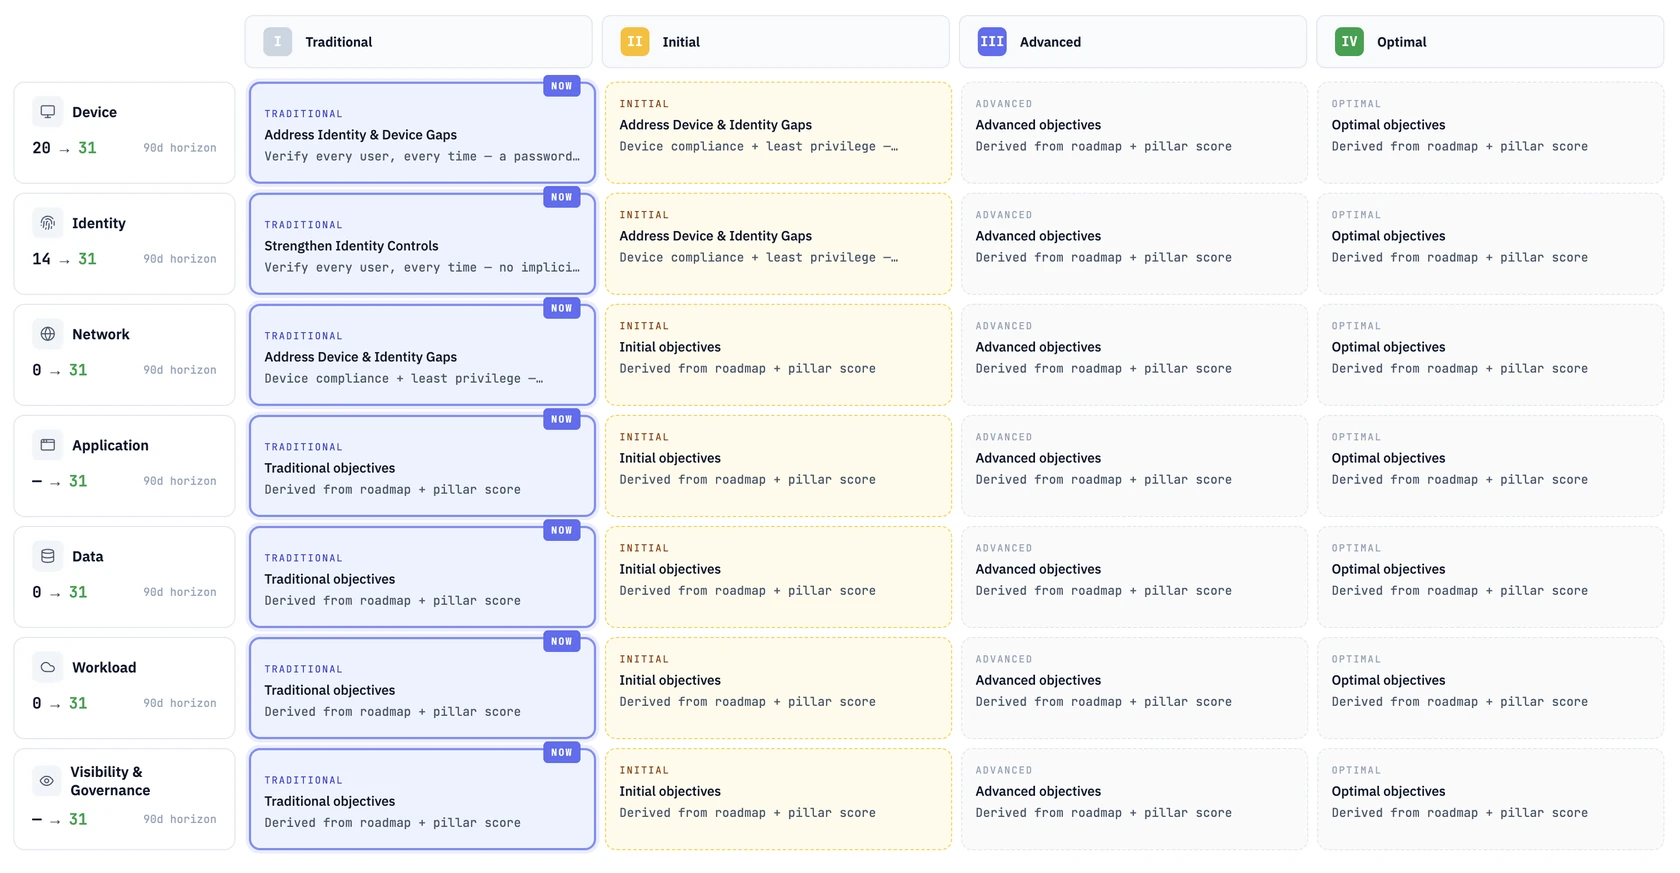
Zero Trust posture
05 · Evidence
Prove
Turn control status and security activity into compliance evidence and audit-ready records.
Control verification results
Security posture status
SSPs
POA&Ms
OSCAL and framework evidence
The checklist says. CoreGuardian finds.
The checklist saysCoreGuardian finds
Illustrative findings based on common control failures.
The platform
One source of truth. Zero blind spots.
Verify every control, continuously.
One reconciled record per asset and identity across 30+ connectors.
Cross-tool contradictions surface as findings: Okta says authenticated, CrowdStrike says the agent is stale.
Zero Trust maturity per pillar from live connector signal, not a survey.